What Does an IP Video Surveillance Compliance Plan for Facilities Need?

Short answer: A facility’s IP video surveillance compliance plan should define why each camera is used, where it may record, who can view or export footage, how long recordings are kept, how audio is handled, and how the network is secured. The exact legal duties depend on the facility, the people recorded, the purpose, and the laws that apply.

IP video surveillance creates more than an image. A camera can produce identifiable footage, send it over a network, store it in a cloud service or recorder, and make it available to administrators in several locations. Facilities need a written process for the whole lifecycle, from installation through access, retention, disclosure, deletion, and system retirement.

This guide is operational, not legal advice. Federal, state, and local requirements can differ by location and use. Have qualified counsel review the rules that apply to your facilities before installing cameras, turning on audio, changing retention, or responding to a request for footage.

Is there one video surveillance rule that applies to every facility?

No. There is no single checklist that resolves every facility’s obligations. Requirements can change with the location, the people recorded, the purpose of the video, the way footage is stored or shared, and whether audio or other sensitive features are used.

A commercial office, school, warehouse, clinic, residential property, and public building may face different rules and policies. A company with sites in more than one state may need a shared operating standard with local additions. The camera system should not be treated as legally compliant just because a vendor offers a privacy setting or a default retention period.

Start by naming the person who owns the policy. That may involve legal, privacy, human resources, IT, facilities, security, records management, and local site leadership. Each team should know which decisions it makes and how a request or incident moves between them.

Create an inventory of every camera and recording stream. For each one, record its location, purpose, view, whether it captures audio, who can access it, where the footage is stored, how long it is retained, and who supports it. A camera without an owner or documented purpose should be reviewed before it remains in operation.

The inventory is also a practical way to find outdated settings. A camera may have been moved, a storage area may have changed, or a former employee may still have access. Review the inventory when facilities change, not only when new equipment is installed.

How should a facility define the purpose and location of each camera?

Write down the purpose of each camera before installation and check that its view matches that purpose. Limit the view to the area needed for the approved business, safety, or security task.

A purpose statement should be specific. “Security” is too broad to guide placement or access. A useful statement might identify a loading entrance, a vehicle gate, a cash handling area, a restricted equipment room, or an exterior approach that needs review after an alarm.

Walk the location with facilities, security, IT, and the teams who use the space. Check the camera angle, lighting, reflections, distance, doors, signs, and nearby areas. A camera pointed at an entrance can capture a wider area than intended. Test the proposed view during normal operating hours and after hours.

Do not place cameras in bathrooms, changing rooms, or other private spaces. Review sensitive areas carefully with counsel and policy owners before use. A camera should not be directed at a neighboring property, private workspace, or employee area unless the purpose and legal basis have been reviewed and approved.

Write a placement record for each device. Include the approved view, the reason for the camera, any privacy mask, the responsible department, installation date, and the review date. If the camera moves or the purpose changes, update the record and repeat the review.

A camera map also helps the organization answer access requests. Staff can identify the relevant recording without guessing which device captured a particular area. It helps service teams restore the intended view if a camera is moved or replaced.

What privacy notice and employee communication should be in place?

Use a notice and communication plan that matches the camera use and the requirements that apply at each location. The facility should explain the purpose of monitoring, identify the office that handles questions, and avoid promising practices the system does not follow.

Signage is one part of notice, not a substitute for policy. Decide where signs belong, who checks them, and how a visitor or employee can ask about the system. If the organization has employee handbooks, visitor policies, or tenant communications, review them for consistency with actual camera use.

Explain the basics in plain language: which areas are monitored, why the organization records video, who can access footage, how to raise a concern, and where to send a records or privacy request. The amount of detail and required form of notice depend on the law and the setting, so counsel should review the plan.

Limit collection to what the facility needs. Do not record more than the stated purpose requires. If a camera’s view has expanded because of construction or a new mounting position, review it before resuming routine use.

Keep a record of approvals and changes. A facility should be able to show who approved a camera, what purpose was documented, when notice was updated, and who reviewed the system later. That record is useful for internal questions and for showing that the organization manages the system deliberately.

Why should audio recording receive its own legal review?

Audio recording can raise legal and privacy questions that differ from silent video, so do not turn on a camera’s microphone by default. Have counsel review the proposed use, location, notice, consent, and state requirements before recording conversations.

Federal law includes restrictions concerning the interception and disclosure of wire, oral, and electronic communications. The current text of 18 U.S.C. § 2511 describes prohibited conduct and specific exceptions. State laws and the facts of a particular recording can affect the analysis. A camera’s audio capability does not establish that recording is permitted.

If the organization has no approved need for audio, disable it and document that choice. If a specific use is proposed, record the business purpose, locations, people who may be recorded, notices, access rules, retention, and review date. Make sure the camera, recorder, app, and cloud settings all reflect the decision.

Do not treat “audio off” as a permanent result if a device is replaced or reset. Include audio settings in installation and maintenance checklists. Recheck the setting after a system update, device replacement, or change to the camera’s configuration.

How should a facility control access to recordings?

Give each person access based on job duties, use individual accounts, and limit export rights to people who need them. The system should record administrator actions and provide a process for approving, documenting, and sharing footage.

Separate the permission to view live video from the permission to search recordings or export a clip. A receptionist may need a live entrance view for a defined task but may not need to download footage. An investigator may need a recorded clip for a specific incident. An administrator may manage accounts but should not automatically have unrestricted access to every recording.

Use a written request path. The policy should identify who receives requests, who verifies authority, who decides which footage is relevant, who approves an export, and how the organization documents the decision. Keep a log of what was shared, with whom, why, and when.

When a clip is exported, preserve the original and record how the copy was created, who handled it, and where it went. The organization should define how it stores files securely and how it prevents an approved clip from being edited or shared outside the stated purpose.

Review user access on a schedule and when someone changes role or leaves. Remove unused accounts. Do not share administrator passwords. Where possible, use multifactor authentication for accounts with remote or elevated access.

How should a facility set video retention and deletion rules?

Set retention through legal, privacy, operational, insurance, and records review. There is no one retention period that fits every facility or purpose. Write down routine deletion, incident preservation, legal holds, access to exports, and the person who owns the process.

Start with the reason the footage exists. A facility may need a short routine period for general areas and a longer hold for a specific incident. Do not choose a long retention period just because storage is inexpensive. Longer retention means more footage to protect, search, and govern.

Define what happens when an event is reported. The right person should be able to identify the relevant camera and time window, preserve the clip before routine deletion, and record why the hold was placed. The policy should also state who can release the hold and when ordinary deletion resumes.

If a service provider stores footage, ask how the organization can retrieve it, export it, preserve it, and delete it. Review who controls storage, how access is logged, where copies may exist, and what happens when the service ends. The contract, system settings, and internal policy should agree.

Test the deletion process. A retention rule that exists only in a policy document may not match system settings. Confirm that the configured schedule works, held footage is not deleted, and deleted footage is not available through an overlooked export or secondary copy.

How should facilities secure IP cameras and recording systems?

Treat cameras, recorders, management software, cloud accounts, and remote support as connected systems that need IT controls. Use a current device inventory, named accounts, supported software, controlled network paths, and a clear process for updates and alerts.

Before installation, document the network path. Show the camera network, recorder, cloud service, administrator devices, remote support, and any integration with access control or alarms. Identify who approves connections and what logs the system provides.

CISA’s Cross-Sector Cybersecurity Performance Goals provide voluntary actions organizations can use to prioritize cybersecurity work. CISA guidance also recommends multifactor authentication for remote access, disabling unused services, and separating network segments where appropriate. Have IT decide how those controls apply to the facility’s video system.

Ask whether the design requires inbound open firewall ports. Alen Security emphasizes video and access system designs that avoid unnecessary inbound firewall holes. That can reduce avoidable network exceptions, but it does not replace review of outbound connections, device security, remote support, authentication, logging, updates, or incident response.

Use unique credentials. Remove default accounts and unnecessary services. Restrict who can change camera settings or add remote users. Confirm that software and firmware updates have an owner and a maintenance process. Set an alert owner for devices that stop reporting.

If the video system connects to other business networks, use the organization’s approved segmentation rules. A camera network should not receive broader access than it needs. Test the connections after changes, and keep a current record of exceptions.

What should a facility’s compliance review cover?

A repeatable review should check camera purpose, placement, notice, audio, users, retention, network security, service access, and open corrective actions. The review should happen on a schedule and when the organization changes a camera, building, purpose, or service provider.

Use a review table that names the owner and evidence for each item:

Review areaQuestion to answerEvidence to keep
PurposeDoes each camera still serve an approved use?Camera inventory and approval record
PlacementDoes the image stay within the approved view?Current view, map, and privacy mask settings
NoticeDo signs and communications match actual use?Sign check and current policy language
AudioIs audio disabled or covered by a current approval?Device configuration and legal review
AccessDo current users need their permissions?User list, role approvals, and access logs
RetentionDo system settings match the written schedule?Retention configuration and deletion test
CybersecurityAre updates, network paths, and support accounts controlled?Network diagram, update record, and review notes
RequestsCan the organization handle access and export requests?Request procedure and sample audit log
Service providerAre storage, access, support, and data return covered?Contract, service plan, and exit procedure

Give every open issue an owner and due date. If a camera’s view no longer matches its purpose, adjust it or suspend it until the review is complete. If a former administrator still has access, remove it and record the correction. A review is useful when it leads to a verified change.

What changes when a school operates the facility?

Schools should add a student privacy and education-record review to the facility’s video policy. A surveillance video may be an education record under FERPA when it is directly related to a student and maintained by the educational agency or a party acting for it.

The U.S. Department of Education’s FAQ on photos and videos under FERPA explains that the same recording can relate to more than one student. It also describes inspection and review rights in situations where a video is an education record. A school should route requests through staff who understand the district’s records process rather than giving a video directly to any person who asks.

Document how school staff handle requests, exports, redaction, disclosure, and emergency exceptions. Train administrators on who can decide whether footage is an education record and who approves a release. The camera system can help locate and protect a clip, but it cannot decide the school’s FERPA obligations.

Schools should also review camera locations, notice, audio settings, access roles, and retention with district counsel and privacy staff. A policy written for a commercial office may not fit student records, school events, or a campus with multiple buildings and student transportation.

What mistakes should you avoid?

Avoid installing cameras without a written purpose, collecting audio by default, keeping footage longer than policy allows, and relying on one shared administrator account. These shortcuts make it harder to explain the system and harder to respond when someone requests footage.

Do not assume a vendor’s default settings match your legal or privacy duties. Do not rely on signage alone to define a program. Do not give all users the same access. Do not leave a camera in place after its purpose or view changes without review.

Do not promise that footage will always be available. A power loss, network issue, storage failure, or configuration problem can interrupt recording. Identify the limitations and test the recovery plan. If a camera supports a safety task, decide what staff should do when it is offline.

Do not use a legal disclaimer as a substitute for a working policy. Ask counsel specific questions about the location, purpose, audio, notice, retention, disclosure, and people recorded. Then make sure the system settings and staff training follow the answer.

Frequently Asked Questions About IP Video Surveillance Compliance

What does IP video surveillance compliance mean?

Short answer: It means the organization uses networked cameras and recordings under rules that fit the location, purpose, people recorded, privacy obligations, retention needs, and cybersecurity requirements. A facility should document camera purpose, placement, access, audio, storage, disclosure, deletion, and system ownership, then review the controls as the site changes.

Is there one federal law for all video surveillance?

Short answer: No single federal rule governs every camera use in every facility. Requirements may depend on the setting, purpose, people recorded, and state or local law. Federal rules can apply to specific issues, such as interception of oral communications or education records. Have counsel review the exact use before deployment.

Can a business record audio with security cameras?

Short answer: Do not turn on audio until counsel reviews the proposed use, location, notice, consent, and applicable state rules. Federal law addresses interception of oral communications, and state requirements can differ. If audio is not needed for an approved purpose, disable it and document the setting.

How long may a facility keep surveillance footage?

Short answer: The right period depends on the purpose, legal and records requirements, and how the footage is used. Set a written schedule with routine deletion, incident preservation, and legal holds. Test that system settings match the policy. Avoid indefinite retention just because storage capacity is available.

Do facilities need signs for security cameras?

Short answer: Notice requirements depend on the location, type of monitoring, and applicable law. A facility should have counsel review signage and employee or visitor communications, then confirm that the language matches actual camera use. Signs do not replace a policy for access, retention, audio, requests, and disclosure.

Can cameras be placed in bathrooms or changing rooms?

Short answer: No. Do not place cameras in bathrooms, changing rooms, or similarly private spaces. For other sensitive areas, review the purpose, view, notice, and legal requirements with counsel and policy owners before installation. A camera’s technical ability to record a location does not make that use appropriate.

Does FERPA apply to school security video?

Short answer: Sometimes. The Department of Education says a surveillance video may be an education record when it is directly related to a student and maintained by a school or someone acting for it. A video can relate to multiple students. District staff should review each request under the school’s privacy and records process.

Who should be able to view or export facility video?

Short answer: Limit access to people whose duties require it. Separate live viewing from recorded search and export when the system allows. Use individual accounts, document approvals, log exports, review permissions regularly, and remove access when a person changes roles or leaves.

How can a facility secure IP cameras from cyber threats?

Short answer: Keep an inventory, use unique accounts, restrict network paths, remove unused services, apply supported updates, use multifactor authentication where available, and control remote support. Ask IT to review the architecture and test logging, alerts, and recovery. Avoid exposing cameras or recorders directly to the public internet.

What should an IP camera privacy policy include?

Short answer: State the purpose and approved locations, notice process, audio rules, authorized users, retention schedule, request and export workflow, service-provider access, cybersecurity controls, and review owner. Include how the organization handles incidents, legal holds, system changes, and camera removal.

Does cloud storage change a facility’s compliance duties?

Short answer: Cloud storage changes where video is stored and how it is accessed, but it does not remove the organization’s responsibility to set purpose, access, retention, disclosure, and deletion rules. Review the service’s permissions, logs, storage, support access, export process, and data return when service ends.

How often should a facility review its camera system?

Short answer: Set a regular review schedule and repeat the review after a camera moves, a facility changes, a policy changes, or the organization changes how it uses video. Check purpose, view, notices, audio, users, retention settings, network access, support accounts, and open corrective actions.

Make the policy match the cameras

A video surveillance program is easier to manage when each camera has an approved purpose, a limited view, a named owner, and rules that match the system settings. Review the whole lifecycle before adding a device or changing how footage is used.

Schedule an IP video surveillance assessment with Alen Security. We can review your camera locations, network path, remote access, storage approach, user roles, and service process with your IT, facilities, and security teams. Call 877-215-2536 or review Alen’s IP video surveillance service.

Keep Learning

About Alen Security

Alen Security designs, installs, and services commercial IP video surveillance and access control for organizations with one or many facilities. The team works with IT, facilities, and security leaders to review camera use, network requirements, user access, and system support.

Sources

How Can You Secure a Commercial Lobby in 2026?

Short answer: Secure a commercial lobby by controlling entry points, confirming visits, applying clear access rules, monitoring entrances, preparing for emergencies, and protecting visitor data. The right setup combines trained staff, practical procedures, access control, video, and ongoing support so visitors can move through the building without unnecessary friction.

What does secure commercial lobby security include?

A secure commercial lobby makes it easy for an expected visitor to reach the right person and difficult for an unapproved person to continue into restricted space. It combines clear entry rules, staff response, visitor records, controlled doors, useful video, and emergency procedures. No single device can make a lobby secure; the outcome depends on how people and systems work together.

Start with a practical rule: every visitor should have a clear path from arrival to approval, direction, and departure. Every exception should have an owner. A person arriving before the host, a delivery driver at the wrong door, a contractor who needs an escort, and a visitor who cannot use a kiosk should not all be handled by guesswork.

CISA’s security planning workbook recommends examining visitor access practices, emergency access for first responders, and facility-specific security procedures. Its guidance is designed for critical infrastructure owners and operators, so use it as a planning reference and adapt it to your building and obligations. The useful principle is to assess the facility as a whole, rather than buying a device before you understand the problem.

Key takeaways

  • Map all entrances and the people who use them, including after-hours arrivals and deliveries.
  • Define who can approve a visit, what areas a visitor may enter, and how exceptions are handled.
  • Connect visitor, door, camera, and emergency workflows only where the integration improves a real task.
  • Collect the minimum visitor information needed, restrict access to records, and define retention.
  • Test the process with staff at the actual entrance and keep a manual fallback ready.

How should you assess lobby risk before choosing security equipment?

Assess the lobby by walking the arrival path from the property line to each destination visitors may reach. Note public doors, loading entrances, side doors, elevator banks, reception sightlines, staff-only corridors, and after-hours routes. The person doing the assessment should observe normal operations, not rely only on a floor plan.

Then list the situations staff must handle: scheduled meetings, unscheduled guests, deliveries, interviews, contractors, after-hours service, an unavailable host, a denied visit, and a system outage. For each one, write the current process and identify the point where staff have to improvise. Those moments often show where a new rule, clearer sign, staff notification, or door change will help more than another device.

Check the building’s existing access control and video coverage. Identify who can unlock the door, how credentials are issued and removed, where video can support a review, and who receives a service call. Document power, network, mounting, lighting, and cabling constraints. For multi-tenant buildings, clarify which decisions belong to the property manager and which belong to each tenant.

Keep the result short enough to use: a marked-up entrance map, a list of visitor types, a responsibility chart, and an issue log. CISA’s Security Planning Workbook offers prompts for reviewing physical security and visitor access. A security integrator can help check how proposed access control, video, and visitor workflows fit the building.

How should a commercial lobby control its entrances?

Use a small number of clearly identified visitor entrances where the building’s layout allows it. Direct expected guests to a visible reception point. Keep employee, loading, and service access separate when operations require different instructions. If a building has multiple public doors, decide which are staffed, which are access controlled, and how a visitor who arrives at the wrong door gets help.

Make the door’s behavior match the approved workflow. Define who can release it, what happens when reception is away, and how staff verify an exception. A door should not be propped open because a badge reader or host notification is inconvenient. If a door must remain open during a defined business period, name the owner, set the time window, and confirm the closing procedure.

At each entrance, make the next action obvious. A visitor should know where to check in, how to contact reception, whether an appointment is required, and what to do if the desk is unattended. Signage is part of the security process: a confusing entrance increases interruptions and encourages people to follow someone else through a controlled door.

For each door, document the normal mode, after-hours mode, loss-of-power behavior, and manual override. Confirm that the response aligns with life-safety requirements and the building’s fire and egress design. Test the actual door, not just the software screen, after installation or configuration changes.

How should visitor check-in work?

A good check-in process confirms the visit, alerts the host, communicates site rules, and records when the visitor leaves. It should be quick for routine arrivals and clear about what happens when something does not match. The system can be paper, digital, or a combination; the important part is that staff know who is responsible for each decision.

When visits are scheduled, provide arrival instructions in advance. Ask the host to confirm the visitor, meeting location, and any escort or access limits. At check-in, match the arriving person to the expected visit using a site-approved method. An invitation or a name on a list should not automatically unlock every door.

Set separate workflows for people whose needs differ. A contractor may need a host, escort, safety briefing, or restricted work area. A courier may need a receiving location and a short stop. A candidate may need a discreet host notification. Someone arriving without an appointment may need staff to verify whether the visit is appropriate before granting access.

For a digital system, test host notifications and badge printing or credential issuance during normal traffic. For a staffed desk, provide a concise checklist and backup contact. In both cases, include an accessible alternative for a visitor who cannot complete the normal check-in step. See the complete guide to visitor management systems for more detail on approvals, records, and rollout.

What should a temporary visitor badge communicate?

A visitor badge should help employees recognize that a person is a visitor and show any instruction that matters, such as escort required or reception check-in complete. Keep the badge design legible from a practical distance, but do not print personal details that the building does not need to display.

Decide whether the badge is visual only or also grants electronic access. If it opens a door, link it to an approval, limit its permissions, and set an automatic expiration. Staff should know how to report a lost badge, deactivate a credential, and check whether a visitor has returned or surrendered it. Avoid reusing credentials without a deliberate reset and assignment process.

Badge rules should not create false confidence. A visitor with a badge may still be in the wrong area or may have exceeded the approved visit. Reception and employees need a simple way to ask for help or confirm a visitor’s host. Combine identification with clear escort and door rules.

For shared lobbies, coordinate badge colors or labels with tenant procedures so staff can understand them without revealing sensitive information. Review the scheme when the building changes tenants, reception coverage, or access-control rules.

How does access control support lobby security?

Access control enforces the building’s door rules after a visitor has been approved. It can help manage employee credentials, restricted spaces, and time-limited access, while a visitor process captures the reason for a visit and the person who approved it. They solve related tasks, but they are not interchangeable.

Map the visitor journey before connecting the systems. Which door, if any, may a visitor use? Who approves that access? Should a visitor receive an escorted credential, or is a staff member expected to release the door? When does access expire? What record should be available afterward? Answering these questions prevents a convenient integration from granting more access than the visit requires.

For organizations with several buildings, a centrally managed system can make it easier to apply consistent credential rules and support practices. Standardization should still allow documented differences in door schedules, local emergency procedures, and tenant responsibilities. A common configuration baseline makes troubleshooting and support simpler.

Network-connected security equipment should be planned with IT. Ask how the system communicates, how user accounts are protected, how updates are managed, and whether installation requires any inbound firewall rule or exposed port. Alen Security’s approach is to configure systems without unnecessary open ports or firewall holes. Review commercial access control and the access control site survey guide before scoping a project.

How can video surveillance support a commercial lobby?

Video can help staff observe entrances, understand an event, and review what happened when an incident or access question arises. It does not replace reception, access control, or a response plan. Useful coverage starts with a specific purpose for each view, such as seeing the approach to a public door or the reception area.

During a site walk, check the lighting at different times, reflections on glass, changes in daylight, ceiling height, signage, and potential obstructions. A camera view that looks clear during installation may be washed out at a bright entrance or blocked by seasonal displays. Confirm that footage can be retrieved by authorized staff and that system time is accurate.

Decide who may view live and recorded video, how to request a review, and how long footage should be retained. The retention period should reflect the business purpose and applicable requirements; do not keep recordings indefinitely by default. Post notices where required and coordinate camera placement with privacy expectations, tenant agreements, and local rules.

Cloud video can support remote review and centralized administration when that fits the organization’s operations. Multi-location teams should define a standard for camera naming, permissions, support, and escalation. Alen Security provides IP video surveillance and can assess whether the lobby’s cameras, network, and access-control events should work together.

How should reception handle deliveries and unannounced arrivals?

Give each arrival type a clear destination and owner. Visitors for a meeting go to reception; deliveries go to receiving; contractors follow the site’s work authorization process; and unannounced guests wait while staff confirm whether the visit is expected. If one desk must handle all of them, provide a short decision tree and backup contact so the person at reception does not have to invent rules.

Do not treat courtesy as authorization. A visitor may be friendly, familiar to an employee, or carrying a parcel and still need to wait for confirmation. Staff should have a polite, repeatable phrase such as, “I’ll confirm your visit before we continue.” The process should support staff who need to decline or delay entry without confrontation.

For a lobby that sees frequent visitors, use host notifications that state who arrived and where the host should meet them. Escalate if the host does not respond within the defined time. Don’t let a visitor tailgate through a controlled door simply because the meeting is scheduled. Use an escort or approved door release when that is the site’s rule.

A reliable welcome matters as much as a control. The process should be easy to understand, consistent across shifts, and supported by training for reception, security, and facilities teams. If the workflow creates a long queue, fix the bottleneck without dropping the approval step.

How should a lobby plan for emergencies?

A lobby emergency plan should tell employees what to do, where to direct visitors, how to communicate, and how designated staff will account for people after evacuation. The process should work when normal systems are unavailable. Maintain a printed or otherwise accessible fallback roster and define who brings it to the assembly point.

The federal emergency action plan standard includes procedures to account for employees after an evacuation. Separate OSHA guidance for warehousing also calls out accounting for workers and visitors in the emergency plan. The exact requirements that apply depend on the workplace and industry, so review the applicable rules and include visitors in the facility’s practical plan. See 29 CFR 1910.38 and the agency’s warehousing hazards and solutions guidance.

Name the person who directs visitors, identifies the assembly area, and shares information with emergency responders. Explain how reception handles a visitor who needs assistance, a person with limited mobility, or an alarm that occurs during check-in. Do not ask employees to put themselves at risk to verify a room or conduct a search.

Run a short drill or tabletop exercise that includes an active visitor, a missing host, a disconnected network, and a desk that is temporarily unattended. Record what caused delay or confusion, assign a fix, and repeat the test after making a change. A roster is useful only if staff know how to retrieve and interpret it.

How do you protect visitor privacy and system security?

Collect the smallest amount of information that supports a defined business need. A visitor record might need a name, host, organization, visit time, and completion status. A facility may have a specific reason to collect additional information, but it should be decided and documented rather than copied from a default form.

Explain the purpose of collection at the point of check-in. Limit access to records by role, use secure accounts, and define a retention schedule. Remove data securely when the approved retention period ends. The Federal Trade Commission’s business guide to protecting personal information recommends keeping information only as long as there is a legitimate business need and using a written retention policy where necessary.

Treat the visitor platform, access-control system, and video equipment as part of the organization’s technology environment. Use named accounts, remove access when staff roles change, keep software and firmware supportable, and coordinate network changes with IT. Ask whether remote access is protected and who can administer it. A cloud service should have an owner, support path, and documented offboarding process.

Privacy and security decisions affect the guest experience. A short, honest explanation is more useful than an unexplained request for personal details. Review forms and permissions when the purpose changes, not only when a system is replaced.

How should lobby controls work across multiple locations?

Set a shared baseline for visit types, approval responsibilities, badge use, access expiration, video review, emergency accountability, data retention, and support. A central view can help a facilities team understand who is authorized and which sites need attention, but local building rules still matter.

Write down what must be the same and what may vary. A site with one staffed entrance may need a different after-hours procedure from a building with a loading dock and several tenant entrances. Record these exceptions in one place so a substitute receptionist or support technician can understand them.

Standardized naming, configuration, and training can reduce confusion when staff cover another location or when an issue needs support. Review access permissions centrally but assign local owners who can confirm whether a visit, employee role, or temporary credential is still valid. Do not assume a credential should automatically work at every building.

An integrator can help assess whether doors, cameras, visitor records, and support processes can be managed simply across sites. Alen Security works with commercial clients on system design, installation, and service, with a focus on a consistent experience that can scale as a business changes. One partner and a clear service path can simplify ownership after installation.

What is a practical lobby security implementation plan?

Use a staged plan so staff can test the workflow before it becomes routine. A small pilot at the main entrance can expose operational problems while they are easy to correct.

  1. Document the current process. List entrances, visitor types, approval steps, staff roles, door schedules, camera views, and emergency procedures.
  2. Set the rules. Decide how to verify visits, issue badges, manage escorts, handle after-hours arrivals, and close each visit.
  3. Confirm technical fit. Check doors, network, power, lighting, mounting, system accounts, support ownership, and integration needs.
  4. Configure the simplest useful workflow. Add only the steps needed for the site’s safety, security, and business purpose.
  5. Train all shifts. Give reception, facilities, IT, hosts, and security staff concise instructions for both normal and exception cases.
  6. Pilot and test. Walk through an expected guest, an unscheduled visitor, a contractor, a denied visit, an emergency, and an outage.
  7. Review records and permissions. Confirm that records are accurate, access is limited, badges expire, and retention is documented.
  8. Assign ongoing ownership. Name who reviews policy, who handles support, who removes obsolete access, and when the process will be reassessed.

Measure operational results rather than counting devices. Track whether guests find the right entrance, how long approval takes, whether badges are recovered or disabled, whether hosts respond, and how quickly staff can find the current roster. Use incidents and staff feedback to improve the process.

When should a commercial lobby security system be updated?

Review the system when the building changes: new tenants, new entrances, different reception hours, higher visitor volume, renovation, new work patterns, or changes to emergency procedures. A system may also need attention when doors are routinely propped open, visitor logs are incomplete, staff cannot find footage, temporary credentials stay active, or support issues repeat.

A review does not automatically mean a full replacement. Sometimes the right fix is a clearer entrance sign, a better host notification, updated training, or a written fallback. At other times, aging readers, camera blind spots, disconnected workflows, or unsupported equipment call for a staged upgrade.

Start with the outcome the facility needs. Then check whether the current system can deliver that outcome reliably and securely. Standardize only after mapping site differences, and keep the final configuration simple enough for staff to use during a busy shift.

How can Alen Security help with commercial lobby security?

Alen Security designs, installs, and services commercial access control and IP video systems. A site assessment can review entrances, doors, visitor check-in, camera views, network conditions, emergency workflows, and support responsibilities together.

For a practical next step, gather the number of entrances, visitor types, staffed hours, existing door and video systems, and any recurring lobby issues. Then contact Alen Security to discuss an assessment. The goal is a lobby process that staff can follow, visitors can understand, and facilities or IT teams can support as the building grows.

Frequently asked questions about commercial lobby security

What is commercial lobby security?

Commercial lobby security is the combination of people, procedures, and systems used to manage entry, identify and direct visitors, protect staff and property, and respond to exceptions. It covers the full path from the property boundary through reception and onward to authorized spaces, then closes the visit at departure.

What are the main layers of lobby security?

The main layers are clear entry rules, controlled doors, a reliable visitor process, trained reception or security staff, useful video coverage, emergency procedures, and secure system administration. Each layer should support the others, with a documented manual fallback for outages and unusual situations.

Do commercial lobby visitors need badges?

A visible temporary badge can help staff distinguish visitors from employees and show whether a guest is expected or escorted. A badge does not authorize access by itself. Set rules for where it works, how long it remains active, who issues it, and how it is returned or disabled.

Can visitor management software replace a receptionist?

Visitor software can organize invitations, approvals, check-in, host alerts, temporary badges, and records, but it does not make judgment calls or welcome a person who needs help. Assign a staff owner and a clear fallback for accessibility needs, denied visits, emergencies, and system outages.

Where should cameras be placed in a commercial lobby?

Place cameras to capture useful views of entry approaches, reception, and relevant doorways without relying on one camera to cover every task. Confirm lighting, sightlines, retention, access permissions, and privacy expectations. A site survey should determine placement and avoid unnecessary collection.

Should visitor management connect to access control?

It can, when the workflow needs approved visitors to receive limited, time-bound access and the systems can enforce the facility’s rules. Define exactly who can approve a visit, which doors are in scope, how credentials expire, and what staff do when an integration is unavailable.

How can a lobby visitor roster help during an emergency?

A current roster can help designated staff identify visitors who may still be on site and coordinate next steps. It should be available to authorized responders or staff at the assembly point, with a manual fallback if power, network access, or the check-in system is unavailable.

What information should visitor check-in collect?

Collect only information needed to verify the visit, notify the host, apply site rules, and support a defined safety or recordkeeping purpose. Explain why information is collected, restrict who can see it, set a retention schedule, and securely remove records when the business need ends.

How often should lobby security be reviewed?

Review it after a renovation, staffing or schedule change, security incident, emergency exercise, or change to visitor volume. A routine review at least annually is a practical baseline, but each organization should set a cadence that fits its risks, obligations, and operating conditions.

What should a 2026 lobby security assessment include?

Assess every public and after-hours entrance, visitor types, host approval, door behavior, camera views, emergency accountability, privacy and retention, network and account security, support ownership, and outage procedures. Record gaps with an owner and a due date, then test the revised workflow at the actual entrance.

cloud-security-schematic

Choosing a Commercial Security Partner for Multiple Sites

How do you choose a commercial security partner?
Choose a commercial security partner that can standardize your locations, coordinate with your IT team, and provide accountable support after installation. Compare network design, access control, video, documentation, training, and the cost of adding your next site.

As an IT Director or Facilities Manager, you are not looking for more dashboards to stare at. You are not looking for more vendors to manage. And you definitely are not looking for another system that promises "visibility" but really creates more noise, more alerts, and more responsibility on your plate.

You already own too much.

You manage infrastructure. You handle uptime. You support users. You think about compliance, continuity, and risk. In many organizations, physical security gets added to that list almost by accident. Suddenly, cameras, doors, credentials, video retention, audit trails, alarms, locksmith needs, and fire life-safety issues all land on your desk.

That is exactly why choosing the right commercial security partner matters so much.

At Alen Security, we believe your security system should help you do your job, not become your job. That idea drives everything we design, install, and support. We build systems for busy professionals. We do not believe the best use of your time is sitting in front of a wall of monitors watching live video all day. That model is inefficient, expensive, and unrealistic for most businesses.

KEY TAKEAWAYS

  • Choose a partner, not just a product supplier. Long-term accountability matters more than a one-time installation.
  • Standardize across sites. Consistent naming, permissions, reporting, and retention settings make support and compliance easier.
  • Protect the network as well as the building. Cloud and hybrid systems should support remote management without requiring inbound open firewall ports.
  • Centralize administration. One coordinated environment reduces overhead and helps you maintain control across multiple locations.
  • Use analytics and automation to reduce manual monitoring. Smart alerts and searchable events are a better fit for busy teams than constant live viewing.
  • Plan for growth. Scalable design prevents rework when you add locations, users, cameras, and doors.

Instead, we focus on practical outcomes:

  • Advanced analytics that help detect meaningful events.
  • Proactive notifications that tell you when action is needed.
  • Smart automation that handles routine responses.
  • Centralized tools that let you manage multiple locations without jumping between platforms.
  • Standardized system design that simplifies support, reporting, training, and compliance.

That approach creates something every overstretched IT Director and Facilities Manager wants more of: control without constant supervision.

If you are evaluating providers for a retail chain, warehouse network, office portfolio, healthcare environment, school campus, distribution operation, or growing multi-location business, this long-form guide will help you make a better decision. It is built around the practical qualities that matter most in the field: a partner who builds real relationships, brings disciplined standardization, protects your environment with a truly secure architecture, gives you centrally managed control, applies hard-earned experience, delivers consistent quality, supports future growth with scalable design, and keeps the day-to-day experience simple enough to run under pressure.

These ideas are not abstract values. They are decision criteria. They affect how fast you can respond to incidents. They affect whether your cloud system creates unnecessary cybersecurity risk. They affect whether your team can generate a clean audit trail under pressure. They affect whether adding a new site is easy or painful. And they affect whether your security investment delivers peace of mind or ongoing frustration.


Why does choosing a commercial security partner feel harder than it should?

Because most businesses are not just buying cameras or door readers. They are choosing a long-term operating model that affects compliance, cybersecurity, investigations, support, and accountability across every location.

The commercial security industry has a reputation for complexity for a reason. Too many projects are sold as disconnected products instead of complete business systems.

One company handles cameras. Another handles access control. A third handles alarms. A fourth handles locksmith work. A fifth handles fire alarm inspections. A sixth "helps" with remote access. Then, when something fails, everyone points at someone else.

That is not a technology problem. It is a partnership problem.

The right security company should not just install equipment. They should reduce vendor sprawl, align systems with your operational goals, and give you a clear, accountable path from planning through support. When you are responsible for multiple sites, multiple stakeholders, and multiple compliance requirements, that level of accountability is not optional.

This is why the best buying decision is rarely about who has the cheapest camera or the flashiest mobile app. It is about whether the provider can help you create a security program that is secure, standardized, manageable, and sustainable.

And for multi-site businesses, the stakes are higher than they first appear.

A commercial security system is not just a set of devices. It becomes part of your operating model. It affects employee entry, visitor handling, incident response, loss prevention, investigations, compliance documentation, and business continuity. It touches your network. It touches your HR workflows. It touches your maintenance process. In some cases, it also touches legal exposure.

That is why the buying process can feel heavier than it should. You are not simply choosing hardware. You are choosing how accountability will work across sites. You are deciding whether standards will be easy to maintain or impossible to enforce. You are deciding whether remote visibility will be convenient and secure, or convenient but risky. You are deciding whether your next three years will be calmer or more chaotic.

The best security partners understand that pressure.

They know your business value goes far beyond the numbers on a quote. They know a missed door event can become an HR issue. They know a weak audit trail can become a compliance issue. They know a poorly deployed camera can become a liability issue. They know a cloud connection designed the wrong way can become an IT issue.

So the real question is not simply, "Who can install this system?"

The real question is, "Who can help us safeguard our people, restrict risk, standardize operations, and prevent this system from becoming another burden?"

That is the lens this guide uses.


Should you use one commercial security partner or multiple vendors?

For most multi-site businesses, one accountable partner is the better choice. It reduces vendor sprawl, shortens troubleshooting, improves consistency, and gives you a clearer path from planning through support.

Relationships matter because physical security is an operational system that touches your buildings, your network, your employees, your visitors, and your compliance posture. If the provider disappears after install, your team is left managing the gaps.

A strong security relationship gives you:

  • A team that understands your environment and history.
  • Better continuity across upgrades, expansions, and service calls.
  • Faster issue resolution because the provider already knows your standards.
  • Less time repeating yourself to different contractors and help desks.
  • More confidence that problems will actually get solved.

At Alen Security, this is why we emphasize end-to-end service. We consult. We design. We install. We maintain.

CONSULT. DESIGN. INSTALL. MAINTAIN.

That matters in practical ways. If your access-controlled opening is having issues, the problem may involve credential rules, reader behavior, door hardware, power, network connectivity, or physical alignment. When those responsibilities are fragmented, support gets messy fast. When they are coordinated by one accountable partner, your life gets easier.

Strong relationships also create strategic value. Over time, a true partner helps you make better decisions about lifecycle planning, standards, and future growth. They can help you answer questions like:

  • Should this next site be cloud, on-premise, or hybrid?
  • Can we reuse any legacy infrastructure without introducing risk?
  • Which locations need higher-priority upgrades?
  • Where are we overcomplicating policy or support?
  • How do we maintain consistency as we grow?

If a security company treats your project like a transaction, expect transactional results. If they treat it like a long-term operational partnership, you get better accountability and better outcomes.

This is where relationships become more than a soft concept. They become a performance advantage.

When your partner knows your naming standards, your network policies, your credentialing rules, your compliance expectations, and your internal stakeholders, projects move faster. Service calls get shorter. Expansion gets easier. Decisions become less reactive. Instead of re-explaining your environment every time something changes, you work with a team that already understands the context.

That is especially important for multi-site businesses. A regional retailer, warehouse operator, or distributed office portfolio does not need six different local opinions and six different ways of doing things. You need consistency backed by people who know your environment well enough to protect it.

Real partnership also creates trust during uncomfortable conversations. Sometimes the right answer is not the cheapest answer. Sometimes the right answer is to replace aging door hardware before it causes recurring downtime. Sometimes the right answer is to phase a project instead of forcing a rushed full rip-and-replace. Sometimes the right answer is to say no to a shortcut that would create cybersecurity or service problems later.

A provider who values long-term relationships will have those conversations honestly.

That matters because your system is not judged on install day. It is judged six months later when an incident happens. It is judged a year later when a site expands. It is judged when HR needs a clean audit trail. It is judged when leadership asks whether your standards are being followed across locations.

A real partner helps you answer yes with confidence.


Why does standardization matter in multi-site commercial security?

Standardization makes security easier to support, easier to audit, and easier to scale. It gives you consistent naming, permissions, retention, reporting, and workflows across every location.

Standardization is one of the most important parts of a strong commercial security program. It is one of the biggest reasons some multi-site environments stay manageable while others become a constant source of confusion.

Without standardization, you end up with:

  • Different camera naming conventions at every site.
  • Different badge formats and permission groups.
  • Different retention settings.
  • Different alert rules.
  • Different hardware generations with different support needs.
  • Different reporting expectations depending on who installed what.

That may sound manageable when you have two or three locations. It becomes a real problem when you have ten, twenty, or fifty.

Standardization gives you operational leverage.

For example, when an HR termination happens, standardized access control rules make it easier to revoke access consistently across all locations. When a compliance issue arises, standardized retention settings and standardized audit trail workflows make it easier to produce records. When a new facility opens, standardized templates reduce deployment time and training time.

This is also where central management becomes more useful. A centralized dashboard is only powerful if the underlying environment is structured well. If every site is configured differently, central management becomes a prettier way to view chaos.

At Alen Security, we help customers create standards around:

  • Camera placement and naming.
  • Door group structure and schedules.
  • Access levels and user roles.
  • Retention policies and export practices.
  • Alerting thresholds and notification workflows.
  • Hardware selection by use case.
  • Expansion planning for future sites.

Standardization is not about making every building identical. It is about creating enough consistency that your systems stay understandable, supportable, and defensible.

That matters for uptime. It matters for onboarding. And it matters for audit readiness.

For busy teams, standardization is one of the fastest ways to reduce friction without reducing capability.

Think about what happens when a location manager reports an issue. If every site uses a different naming structure, different device mix, different credential rules, and different reporting expectations, your team spends its time translating. Translation is wasted effort. It slows support. It creates mistakes. It weakens accountability because no one is sure whether Site A is supposed to work like Site B.

A standardized environment fixes that.

It gives you common language. It gives you repeatable workflows. It gives you cleaner training. It gives you more reliable escalation. It also gives you a stronger compliance posture because your audit trail is not dependent on each location improvising its own process.

This matters in industries with strict operational expectations. Warehouses need consistent restricted-area access. Retail chains need repeatable store opening and closing workflows. Multi-tenant offices need structured credential management. Distribution centers need camera coverage that follows the same logic from site to site so investigations are not reinvented every time.

It also matters financially.

Without standards, every site becomes a small custom project. Custom projects cost more to support. They cost more to document. They cost more to troubleshoot. They often cost more to expand. Standardization protects your investment by making future decisions easier.

That is one reason we talk so much about simplicity. Simplicity does not happen by accident. It is often the result of disciplined standardization done well.


Should cloud security systems require open firewall ports?

No. Modern cloud and hybrid security systems should deliver remote visibility and control without requiring inbound open firewall ports that expand your attack surface.

This pillar deserves extra attention.

Modern physical security systems are connected systems. Cameras are IP endpoints. Access control platforms live on your network. Cloud management touches identity, devices, logs, and remote administration. That means your physical security platform can either support your cybersecurity posture or undermine it.

The wrong design can create risk fast.

When evaluating a provider, ask a simple question: Does your cloud access or cloud video solution require inbound open firewall ports?

If the answer is yes, keep digging.

Busy IT professionals do not want to punch holes in the firewall just to make a security product work. And they should not have to. Cloud convenience should not come at the cost of increased exposure. Secure remote connectivity should be designed to reduce attack surface, not expand it.

At Alen Security, we strongly emphasize solutions that do not require inbound open firewall ports for cloud access control or cloud video workflows. That supports a cleaner, more secure architecture while still giving authorized users the remote visibility and administrative control they need.

That is a practical security advantage.

It means:

  • Less unnecessary external exposure.
  • Better alignment with modern IT security expectations.
  • Fewer exceptions for your team to defend internally.
  • Stronger confidence that your physical security tools are not creating cyber liabilities.

Security also includes device health and lifecycle management. Ask your provider:

  • Are the products NDAA compliant where appropriate?
  • How are firmware updates handled?
  • How are vulnerabilities monitored and remediated?
  • What logging is available for administrative actions?
  • How is user access controlled and audited?
  • What happens when devices go offline or fall behind on updates?

A good security integrator should be comfortable having this conversation with your IT team. If they only want to talk about resolution, frame rates, and card readers, they are missing the bigger picture.

Physical security should not be the back door into your environment. It should be designed to safeguard people and property without weakening network security.

This is where being secure has to mean more than encrypted marketing language.

It should mean the architecture respects your IT policies. It should mean remote access is thoughtfully designed. It should mean permissions are controlled, administrative actions are logged, and devices can be maintained without guesswork. It should mean your provider understands that every connected camera, controller, and appliance becomes part of a broader risk conversation.

That is why security and quality are closely tied together. A poor install is not just messy. It can create unmanaged devices, inconsistent configurations, weak documentation, and avoidable exceptions that put your team in a difficult position later.

A secure design also supports faster incident response. When you know who has access, what changed, when it changed, and where to find the relevant logs, you are in a much stronger position to investigate issues. That is the value of a clean audit trail. It is not just a compliance phrase. It is the record that helps you establish accountability under pressure.

And just as important, secure design should not make the system harder to use. The right partner protects the environment and keeps the experience simple enough for daily operations.

That balance matters.


What are the benefits of centrally managed security for multiple locations?

Centrally managed security helps you control users, doors, video, schedules, and reporting across all sites from one environment. That reduces overhead, improves response time, and keeps standards consistent.

Central management is one of the biggest quality-of-life improvements a modern commercial security program can deliver.

If your team is managing separate systems at each site, the overhead adds up fast. Different logins. Different video interfaces. Different badge workflows. Different support paths. Different reports. Different procedures when something goes wrong.

That model does not scale.

A centrally managed environment allows you to:

  • Administer users across multiple sites from one interface.
  • Revoke or change credentials quickly across the organization.
  • Review events without physically going to each location.
  • Standardize permissions, schedules, and reporting.
  • Support regional and nationwide operations more efficiently.
  • Reduce the time it takes to investigate incidents.

This is especially important for retail, distribution, and portfolio-style businesses. If you are responsible for dozens of doors and hundreds of cameras across multiple states, fragmented management becomes its own operational risk.

But central management should not be confused with central babysitting.

This is where we need to be clear: we do not believe busy professionals should spend their day watching live video feeds.

That old-school model sounds reassuring, but in most commercial environments it is not realistic and it is not efficient. The better model is event-driven awareness.

That means your system should help surface what matters through:

  • Motion and object analytics.
  • Smart search tools.
  • Exception-based notifications.
  • Door held open alerts.
  • Access denied trends.
  • Unusual after-hours activity flags.
  • Camera health notifications.
  • Automated reporting.

Instead of forcing you to stare at screens waiting for something to happen, the system should tell you when an event meets the threshold for attention. That is a much better fit for how real IT Directors and Facilities Managers work.

You should be able to focus on your job while the system handles the routine monitoring layer in the background.

That is what central management looks like when it is designed for real operations.

For multi-location organizations, being centrally managed is not a luxury. It is how you preserve control as the footprint grows.

Without central administration, every task takes longer. New hires require site-by-site updates. Terminations require manual cleanup in multiple places. Incident reviews become scavenger hunts. Reporting becomes inconsistent. Even small tasks expand into process overhead because the environment is fragmented.

Central management changes that. It gives you one place to restrict access, review activity, confirm policy, and maintain standards. It supports accountability because more actions are visible and easier to verify. It supports relationships because your provider can support the whole environment instead of treating each location like an isolated exception.

And when the system is paired with smart analytics, central control becomes more powerful.

You do not need people parked in front of screens. You need the platform to surface meaningful exceptions. You need health alerts when a device goes offline. You need notifications when a door is held open too long. You need searchable video and event data that lets you move from question to answer quickly.

That is a much more disciplined model than manual screen monitoring.

It protects attention, which is one of the scarcest resources your team has.


Why does experience matter when choosing a commercial security integrator?

Experience helps a provider anticipate real-world issues before they become expensive problems. It improves planning, modernization, deployment quality, and long-term support.

Experience matters because security systems live in the real world, not in the demo room.

Buildings have quirks. Networks have constraints. Users have habits. Weather matters. Traffic flow matters. Shift schedules matter. Local code matters. Existing infrastructure matters. Growth plans matter.

A provider with decades of experience sees these issues early. They ask better questions. They recognize patterns faster. They know when a low-cost shortcut will create a high-cost problem later.

At Alen Security, our 50+ years of experience are not just a number. They show up in practical decisions every day:

  • Designing systems that work in demanding commercial environments.
  • Recommending hardware that holds up over time.
  • Coordinating disciplines like video, access, intrusion, locksmith work, and fire systems.
  • Anticipating support needs before they become emergencies.
  • Helping customers balance capital cost, operating cost, and long-term maintainability.

Experience is especially valuable when you inherit an outdated or inconsistent environment. Many IT and facilities leaders do not get to start from scratch. They inherit old DVRs, unsupported cameras, different badge systems, unreliable door hardware, inconsistent user permissions, and compliance concerns that have been building for years.

That is where an experienced partner can bring order.

They can help you decide what should stay, what should go, what can be integrated temporarily, and what needs immediate replacement. They can help you prioritize risk instead of trying to replace everything at once. And they can help you create a realistic roadmap, not just a wish list.

Experience gives you confidence that the provider has solved problems like yours before.

In commercial security, experience protects you from learning the hard way.

An inexperienced provider may be able to sell a platform. That is not the same as understanding how to deploy it cleanly across real buildings with real constraints. They may not spot the wiring problem that will hurt reliability later. They may not anticipate how a warehouse environment changes camera selection. They may not understand how credential policies need to work differently for executives, contractors, temporary staff, and regional managers. They may not coordinate properly with locksmith work, door hardware, intrusion, or fire alarm obligations.

Those gaps add up.

Experience also matters during modernization. Most organizations are not starting from a blank page. They are living with a mix of old and new. They may need to phase capital spending. They may need to preserve uptime during migration. They may need to support a business opening schedule while systems are upgraded in the background.

That is where decades of field experience are valuable. An experienced partner can sequence work properly. They can flag dependencies early. They can prevent a rush to deploy technology that looks good in a demo but creates friction in the field.

That practical judgment is easy to overlook during procurement. It becomes obvious later.

When a provider has seen enough environments, they stop designing for the sales presentation and start designing for the operating reality. That is the kind of experience that creates peace of mind.


What does quality look like in a commercial security installation?

Quality means more than hardware. It includes clean design, proper camera placement, reliable door hardware integration, stable network coordination, documentation, testing, training, and responsive support.

Quality is not only about which brand of camera gets installed. It is about the total system.

A high-quality commercial security deployment includes:

  • Clean, intentional design.
  • Proper hardware selection for the use case.
  • Thoughtful camera placement.
  • Reliable door hardware integration.
  • Good documentation.
  • Tested workflows.
  • Clean cable management.
  • Stable network integration.
  • Clear end-user training.
  • Responsive service after go-live.

Poor quality shows up everywhere. Cameras placed too high to capture useful detail. Doors that look "installed" but do not close consistently. Credentials that are hard to manage. Alerts that trigger too often to be trusted. Incomplete documentation. Messy support handoffs.

Quality also affects adoption. If the system is unreliable or confusing, your team stops trusting it. Then you lose one of the most important benefits of a modern security platform: confidence.

That is why we take an end-to-end view of quality. It should be evident from consultation through ongoing support. The quality of the install affects the quality of the data. The quality of the data affects the quality of the analytics. And the quality of the analytics affects whether your team gets useful notifications or just noise.

This is one more reason we do not promote a "watch live video all day" philosophy. If your only operational strategy is constant manual observation, you are compensating for weak system design. A quality system should help automate awareness through reliable events, smart analytics, and clean workflows.

In short: quality is not an upgrade. It is the difference between a system that helps and a system that drains time.

For us, quality is tied directly to trust.

If cameras do not capture usable detail, you do not trust the footage. If the access control workflow is clumsy, you do not trust the permissions. If door hardware fails inconsistently, you do not trust the opening. If alerts are noisy and poorly configured, you do not trust the event feed. And when trust drops, people start creating workarounds.

Workarounds are dangerous.

They lead to badge sharing. They lead to manual logs. They lead to unsupported remote access habits. They lead to delayed investigations because no one is sure where the right data lives. A quality system prevents those behaviors by making the right process the easiest process.

That is why quality also includes documentation, training, and service. The install is only one moment in the system lifecycle. The real test is whether the system continues to perform, whether your team knows how to use it, and whether support is responsive when conditions change.

Quality protects uptime. It protects accountability. It protects the credibility of the entire security program.

And for multi-site businesses, quality must be repeatable. A single flagship location with a polished install does not solve the bigger challenge. You need consistent quality across the whole footprint so every site supports the same standard of confidence.


How do you choose a commercial security system that can scale?

Choose a system with repeatable standards, centralized management, secure architecture, and workflows that can expand without forcing a redesign every time you add a new location.

Scalability is not just about whether the software can technically support more devices. It is about whether your people, processes, and support model can support growth without multiplying friction.

A scalable security program should let you:

  • Add locations without reinventing policy.
  • Add doors and cameras without rebuilding administration.
  • Add users without creating permission chaos.
  • Expand reporting without complex manual work.
  • Preserve standards as the footprint grows.
  • Support remote management across regions.

This is where the eight pillars work together. Scalability depends on relationships, standardization, secure architecture, central management, experience, quality, and simplicity. If any of those are missing, growth gets messy.

For example:

  • If you lack standardization, each new location becomes a custom project.
  • If you lack central management, each new site adds administrative overhead.
  • If you lack simplicity, training burden grows with every expansion.
  • If you lack secure architecture, cloud growth may introduce unacceptable cyber exceptions.
  • If you lack relationship continuity, support quality drops as the environment expands.

We often talk to businesses that started with a few standalone systems because that was "good enough at the time." Then the company added more sites, more employees, more compliance demands, and more risk. Suddenly the original decisions become operational bottlenecks.

A scalable strategy avoids that trap.

Whether you manage a single warehouse today or a regional retail network tomorrow, your security environment should support growth without forcing a total reset.

Being scalable means planning for the next site before it becomes urgent.

That does not mean overbuilding. It means making deliberate decisions now so future growth is not punished later. It means selecting platforms that support expansion cleanly. It means using templates, standards, and permission structures that can be repeated. It means thinking about how reporting, support, and administration will work when the footprint doubles.

Scalability is also about preserving simplicity over time.

Some systems appear affordable because they solve the immediate need at one location. But once you add more sites, they create management sprawl. More interfaces. More manual steps. More local exceptions. More training. More troubleshooting. The real cost shows up later in labor, inconsistency, and slower response.

A scalable design prevents that by creating a framework your business can grow into.

That matters for regional and nationwide retail. It matters for warehouse networks. It matters for office portfolios. It matters for any business that may add locations, change operating hours, expand headcount, or face new compliance obligations.

Growth should not force you to start over.


Why is simplicity important in commercial security systems?

Simple systems are easier to use under pressure. They reduce manual steps, improve consistency, speed up incident response, and help busy teams stay in control without becoming security specialists.

Simplicity is often misunderstood. It does not mean basic. It means usable.

A simple security program can still be highly capable. In fact, the best systems often feel simple precisely because the complexity is handled well behind the scenes.

For a busy IT Director or Facilities Manager, simplicity means:

  • Clear interfaces.
  • Logical permissions.
  • Repeatable workflows.
  • Useful alerts.
  • Fewer manual steps.
  • One accountable support path.
  • Less need to remember site-by-site exceptions.

Simplicity matters during routine operations, but it matters even more during stressful moments. When an incident happens, nobody wants to dig through five systems and three manuals just to export footage or verify a door event. You need clarity.

That is why we build for operational simplicity:

  • Search video quickly.
  • Review meaningful events fast.
  • Produce audit trails efficiently.
  • Manage credentials without confusion.
  • Get notified when intervention is needed.
  • Trust the system to handle the rest.

Again, that means we lean into analytics, automation, and proactive notification instead of requiring constant live monitoring.

DETECT. NOTIFY. RESPOND. RETURN.

That is the rhythm busy professionals need. Detect what matters. Notify the right people. Respond appropriately. Return to the work that actually drives the business.

In a strong commercial environment, simple is not a compromise. It is a design goal.

The right system should reduce the number of decisions your team has to make in the middle of a busy day. It should make common tasks obvious. It should make rare but important tasks manageable under stress. It should help you restrict access, find events, export evidence, and verify actions without needing a specialist for every step.

This is where simplicity and relationships intersect. A provider who knows your environment can help keep workflows clean over time instead of layering on exceptions until the system becomes hard to use.

It is also where simplicity and standardization intersect. Repeatable naming, repeatable permissions, repeatable reporting, and repeatable support paths are what make the environment feel understandable instead of fragile.

And just as important, simplicity supports accountability. If a system is too confusing to operate, important steps get skipped. If it is clear, your team is more likely to follow policy consistently.

Simple systems get used. Used systems create value. That is the point.


Why do advanced analytics matter more than live monitoring?

Network integration and security server rack

Yes. In most commercial environments, analytics, proactive notifications, and smart search are more effective than expecting busy teams to constantly watch live video feeds.

One of the biggest mindset shifts in commercial security is moving from passive recording and manual observation to active intelligence.

Traditional thinking says more screens equal more security. In reality, more screens often just mean more information that nobody has time to process. Most organizations do not have dedicated personnel sitting in front of video walls all day, and even if they did, people are not great at maintaining constant vigilance across dozens of feeds for hours at a time.

That is why we believe smarter systems beat constant watching.

Advanced analytics can help identify:

  • Unusual motion patterns.
  • Loitering in restricted areas.
  • After-hours activity.
  • Vehicle or object attributes.
  • People entering specific zones.
  • Occupancy trends.
  • Access anomalies.
  • Searchable event patterns that speed investigations.

This makes video more actionable.

Instead of asking someone to remember when an incident may have happened, you can search by event type, motion, time window, direction, object trait, or related access event. Instead of waiting for someone to notice a problem live, the system can send a proactive notification when a threshold is met.

This is a better use of both technology and human attention.

For multi-site businesses, that matters even more. If you are responsible for a retail chain, a distribution portfolio, or multiple offices, live monitoring across every site is not realistic. Event-based awareness, centralized search, and automation are.

This approach also improves accountability. When the system is designed around exceptions, analytics, and documented workflows, the resulting audit trail is stronger. You can show what happened, when it happened, what triggered a notification, and how your team responded.

That is operational value. That is compliance value. And that is peace of mind.

This point is worth underscoring because it changes how you should evaluate a partner.

If a provider talks as if security effectiveness depends on people staring at screens all day, they are describing an outdated operating model for most commercial organizations. It sounds reassuring, but it usually creates labor cost, alert fatigue, and false confidence. Human attention is limited. Even well-intentioned teams miss things when they are asked to watch too much for too long.

Intelligent analytics are different.

They help the system do the first layer of work. They flag anomalies. They accelerate searches. They connect related events. They reduce the time between an incident and a response. They also make your environment more defensible because actions are based on defined thresholds and documented activity, not vague recollection.

That does not mean people are removed from the process. It means people are reserved for the moments that actually require judgment.

That is a far better model for a time-poor IT Director or Facilities Manager.

You should not have to babysit your system to get value from it. The system should help deter, detect, restrict, and prevent while giving you the confidence that the right information will surface when needed.

That is what modern commercial security should look like.


How do you evaluate a commercial security partner?

If you are comparing vendors, ask questions that map directly to the operating realities above, not just the feature sheet.

RELATIONSHIPS

  • Will you be our long-term support partner or just the installer?
  • Do you use sub-contractors for key parts of the job?
  • Who owns the outcome when something fails?
  • How do you stay aligned with our internal stakeholders over time?

STANDARDIZATION

  • How do you help multi-site customers create consistent naming, permissions, and reporting?
  • Can you standardize new sites using templates and repeatable workflows?
  • How do you support audit trail consistency?
  • What standards do you recommend across cameras, doors, schedules, and user roles?

SECURE

  • Do your cloud video and cloud access solutions require inbound open firewall ports?
  • How do you handle firmware updates and vulnerability response?
  • What cybersecurity practices are built into your design approach?
  • How do you protect remote administration without weakening our network posture?

CENTRALLY MANAGED

  • Can we manage users, doors, schedules, video, and reporting from a single platform or coordinated interface?
  • How do you support remote administration across multiple locations?
  • How do you reduce alert noise?
  • How do you help teams investigate incidents across sites without switching tools constantly?

EXPERIENCE

  • How long have you been serving commercial clients?
  • What types of environments have you deployed in?
  • How do you approach modernization when legacy systems are involved?
  • What have you learned from similar multi-site projects that would apply to us?

QUALITY

  • What does your install and testing process look like?
  • How do you document the final environment?
  • What makes your workmanship and support different?
  • How do you validate that analytics, notifications, and workflows are tuned correctly before handoff?

SCALABILITY

  • How does this system handle additional sites, users, doors, and cameras?
  • Will we need to redesign our environment when we grow?
  • How do you help customers plan for phased expansion?
  • How do you preserve standards as more locations come online?

SIMPLICITY

  • How intuitive is the administrative workflow?
  • How much training will our team need?
  • How do you ensure the system helps busy professionals instead of creating more overhead?
  • How do you reduce the number of manual steps required for common tasks?

A provider who can answer these questions clearly is far more likely to deliver a system that works in the real world.

And pay close attention to how they answer, not just what they answer.

Do they sound like they understand operations, compliance, and support? Do they speak comfortably about both physical security and network security? Do they understand that your team needs visibility without complexity? Do they naturally talk about accountability, repeatability, and lifecycle planning?

Those signals matter.


What should the right security partner deliver?

By the end of your evaluation, the right commercial security partner should be able to deliver a clear picture of how they will help you:

  • Protect people, property, and operations.
  • Avoid unnecessary cyber exposure.
  • Centrally manage multiple sites.
  • Standardize workflows for compliance and support.
  • Reduce vendor sprawl.
  • Use analytics and automation instead of relying on nonstop live monitoring.
  • Scale with your business.
  • Keep day-to-day administration simple.

That is the real goal.

Not more complexity. Not more screens. Not more noise.

More control. More confidence. More accountability. More time back.

A strong partner should also be able to show you how all of those benefits work together.

Relationships make service and planning smoother. Standardization makes support and compliance easier. Secure architecture protects your network without taking away flexibility. Central management reduces overhead across the footprint. Experience helps you avoid expensive mistakes. Quality creates trust in the system. Scalable design protects future growth. Simplicity makes the whole environment easier to run.

That is how a security program becomes sustainable.

It stops being a patchwork of products. It becomes an operating system for protection, accountability, and peace of mind.

For busy leaders who inherited physical security on top of everything else, that is the outcome that matters most. You do not need more moving parts. You need one trusted partner who can simplify the environment, protect the business, and help the system quietly do its job in the background.

That is what good commercial security should feel like.


What do the best commercial security partners consistently get right?

CapabilityWhy It Matters To You
Strong relationshipsYou get a trusted partner who knows your environment and stays accountable over time.
Standardized deliveryConsistency across sites improves support, training, compliance, and audit trail quality.
Secure architectureCloud access and video should not require inbound open firewall ports that increase exposure.
Centralized managementOne interface and one strategy reduce friction across multiple locations.
Proven experienceDecades of real-world delivery help prevent mistakes and support better decisions.
High-quality executionBetter design, installation, documentation, and service produce stronger long-term results.
Scalable designThe system can grow with your footprint without creating new management problems.
Operational simplicityBusy professionals need useful alerts, intuitive workflows, and less manual oversight.

If you remember nothing else from this guide, remember this: the right commercial security partner helps you create an environment that is secure, manageable, repeatable, and ready for growth. They help you safeguard the business without overwhelming the people responsible for running it.


FREQUENTLY ASKED QUESTIONS

Keep it simple. You want a partner that reduces complexity while improving control. The big things to look for are strong relationships, standardization across sites, secure cloud architecture that does not require inbound open firewall ports, centralized management, proven experience, quality delivery, scalability, and simplicity.

Why are relationships so important in commercial security?

Because physical security is not a one-time purchase. It becomes part of your day-to-day operation. A strong partner understands your sites, standards, and priorities over time, which leads to faster support, clearer accountability, and fewer gaps between design, installation, and service.

How does standardization help multi-site businesses?

Standardization creates consistency across camera naming, user roles, access levels, retention settings, alert workflows, and reporting. That makes training easier, support faster, new site deployment smoother, and audit trail requests easier to handle.

Why does Alen Security emphasize that cloud systems should not require open firewall ports?

Because cloud convenience should not come with extra network exposure. Solutions that do not require inbound open firewall ports help reduce attack surface while still giving authorized users secure remote visibility and management.

What does centrally managed security actually look like in practice?

It means you can manage users, credentials, doors, schedules, video, and reporting across multiple locations from one coordinated environment. That cuts site-by-site overhead, improves response speed, and helps keep standards consistent as you grow.

Why does Alen Security focus on analytics and notifications instead of expecting customers to watch live video all day?

Because most busy professionals do not have time to sit in front of screens waiting for something to happen. Advanced analytics, proactive notifications, and smart automation help surface the events that matter so you can respond when needed and get back to your real work.

How does experience improve the outcome of a commercial security deployment?

Experience helps a provider spot real-world issues early, recommend durable solutions, work around inherited limitations, and design systems that hold up over time. That helps prevent costly mistakes during planning, installation, modernization, and support.

What does quality mean in a commercial security system?

Quality is more than hardware. It includes system design, camera placement, door hardware integration, network coordination, documentation, testing, training, and post-install support. A quality deployment is easier to trust, easier to use, and less likely to create recurring service problems.

Why is scalability important even for companies with only a few sites today?

Because growth can happen fast. A scalable system lets you add locations, users, doors, and cameras without rebuilding your standards, changing your management model, or creating more admin work later.

What makes Alen Security a fit for busy multi-site organizations?

We design commercial security systems around simplicity, accountability, and long-term performance. With over 50 years of experience, end-to-end service, centralized cloud and hybrid options, strong cybersecurity priorities, advanced analytics, and support for video, access, intrusion, locksmith, and fire alarm needs, we help busy teams stay protected without turning security into a full-time job.


Discuss your sites with a commercial security partner

Stop juggling multiple vendors and outdated systems. You have enough on your plate. Let us simplify your security so you can focus on the rest of your job while the system helps handle the routine work.

CONSULT. DESIGN. INSTALL. MAINTAIN.

Discuss your commercial security needs with Alen Security
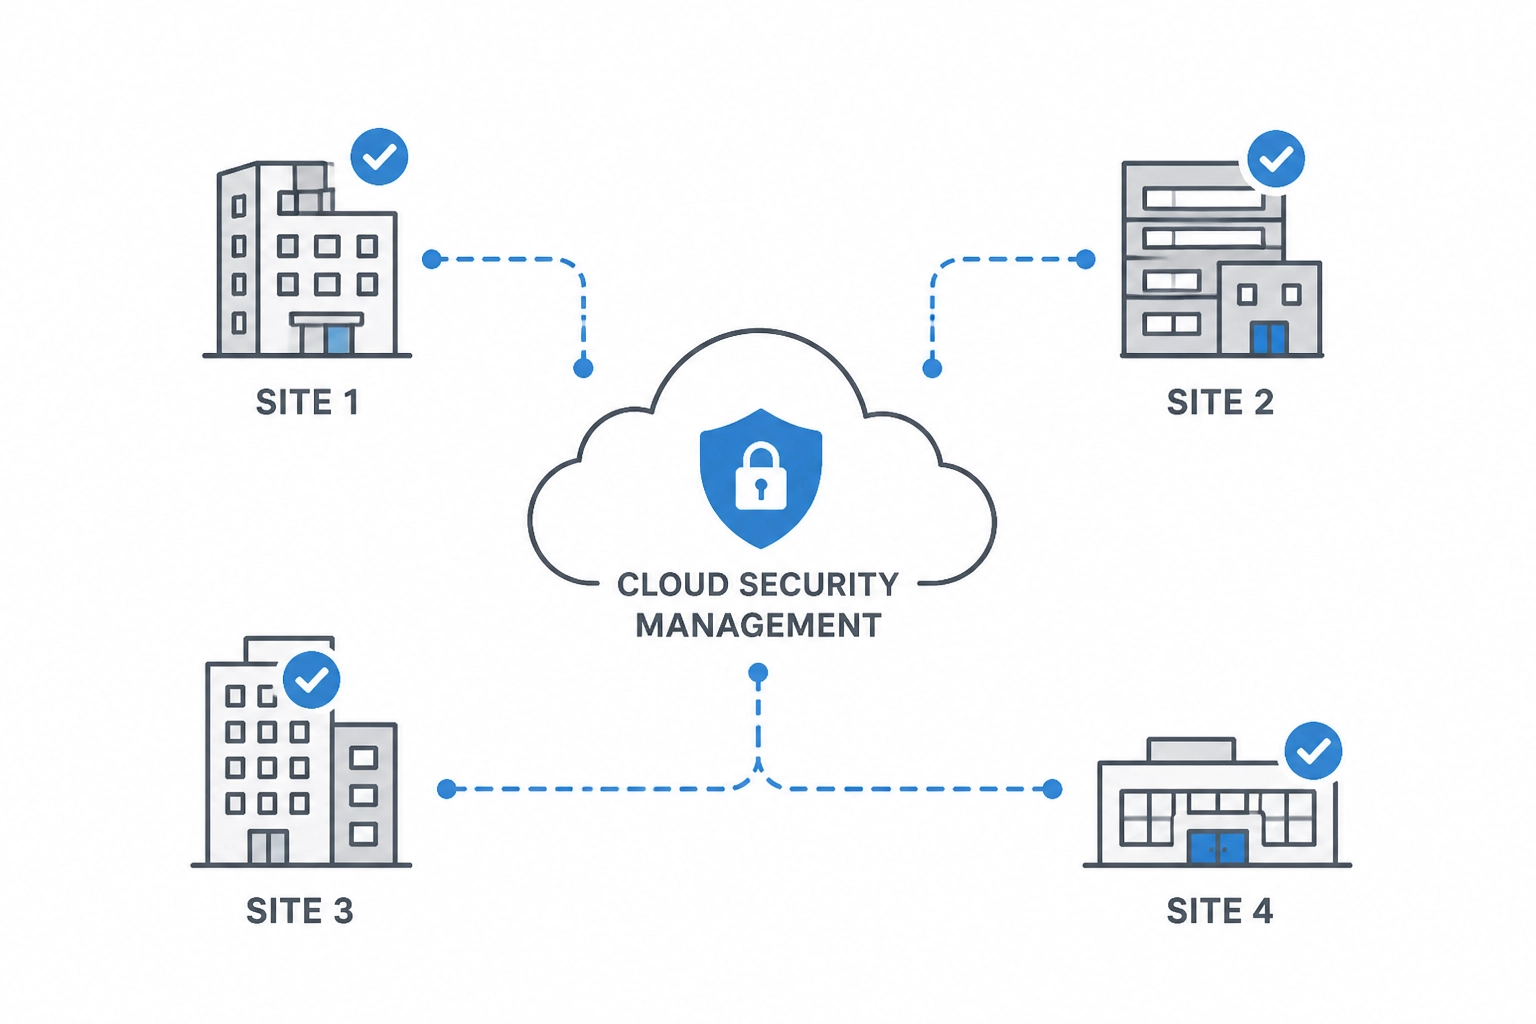
Is Your Access Control System Secure? IT Checklist

By Alen Security’s Dr. Tierney

Is Your Access Control System Secure?

Your access control system connects your doors to software, administrator accounts, and, often, your company network. If you’re responsible for IT across several locations, you need to know who can change that system, how it communicates, and what happens when something stops working.

An access control cybersecurity review should cover system architecture, administrator permissions, network connections, reader security, software updates, remote support, integrations, and recovery. Start by documenting those areas, then confirm that the actual installation meets your company’s requirements.

That gives you something useful to work with when a vendor says the system is secure. You can ask how, see the evidence, and decide what needs attention.

Key takeaways

  • Cloud, on-premises, and cellular systems all need defined security controls and clear ownership.
  • Administrator accounts deserve close attention because they can change permissions across many doors or locations.
  • An encrypted connection to the cloud doesn’t tell you whether communication between the reader and controller is protected.
  • Offline operation needs testing, especially when a credential is revoked while a site is disconnected.
  • A shared standard makes reviews and support more manageable as you add locations.

Can an access control system create cybersecurity risk?

Yes. Connected physical access control systems can introduce risk through weak administrator accounts, unsupported software, exposed network services, insecure remote support, or integrations with excessive permissions. The level of risk depends on the equipment, configuration, and how people manage it.

Picture an office where the doors work perfectly, but a former service provider still has an active administrator account. Nobody notices a problem during the morning badge check. The account still deserves attention because it may allow someone to change schedules, issue credentials, or remotely open doors.

NIST’s Zero Trust Architecture, SP 800-207, explains that network location or ownership alone should not establish trust. Applied to physical security, that means a controller sitting inside your firewall still needs appropriate authentication, permissions, and maintenance.

You don’t need to assume the system is unsafe. You need enough information to assess it.

Where should an access control cybersecurity review start?

Start with a current architecture diagram and an equipment inventory. Together, they should show what runs at each location, where management happens, and which connections cross into other systems.

For a multi-site business, document the approved design and any locations that operate differently. Otherwise, a review of headquarters can miss the older server still running at an acquired office.

Map the equipment and connections

Ask your integrator to identify the controllers, readers, management platform, servers, databases, and network segments. Include cellular connections, remote support tools, mobile administration, and integrations with identity or video systems.

The diagram should show which way traffic flows and where authentication happens. Pair it with the required ports, protocols, destinations, encryption settings, and supporting services, including DNS and time synchronization.

Record who owns each part

Your inventory should include equipment models, firmware versions, support status, site locations, and the person or team responsible for maintenance. Document where controllers, power supplies, switches, and related cabling are installed, along with who can physically reach them.

This also helps during service calls. Your IT team shouldn’t have to track down the person who remembers which closet contains the panel.

Who should have administrator access?

Give each administrator an individual account, require multi-factor authentication where supported, and limit permissions to their responsibilities. Establish a process for approving access, reviewing it, and removing it when someone leaves or changes roles.

Central management can make a large portfolio easier to support. It also means a broadly privileged account may affect many locations, so those permissions need deliberate limits.

Match permissions to everyday tasks

A site manager may need to issue replacement badges for one office. A regional security manager may need visibility across several locations. Neither automatically needs permission to change integrations or create global administrators.

Separate credential management, door commands, reporting, configuration, and administrator management wherever the platform supports it. Ask the vendor to demonstrate the roles you expect to use.

Include service providers and emergency accounts

Review vendor accounts alongside employee accounts. Confirm who approves them, whether they expire, and how you disable them when a technician or service partner changes.

If you maintain an emergency administrator account, protect it, monitor its use, and document when it may be accessed. A shared password that everyone knows makes it harder to establish who changed the system.

How should access control connect to your network?

Access control network connections should follow documented traffic requirements and your company’s segmentation policy. IT should approve the necessary communication paths and restrict unnecessary access between the security system, the internet, and other business systems.

Ask for the platform’s actual network requirements before installation. A general statement that it “works with your firewall” doesn’t give your team enough information to approve the design.

Confirm inbound and outbound requirements

For a platform designed around outbound encrypted connections, confirm whether any inbound firewall rules or port forwarding are required. Review the specific destinations, protocols, authentication, certificate handling, and update paths.

Avoid unnecessary inbound exposure. Even when a design requires no inbound port forwarding, administrator accounts, device software, and integrations still need review.

Make segmentation enforceable

A dedicated VLAN can help organize access control equipment, but separation also depends on the rules governing traffic between networks. Define which systems can communicate with the controllers and management platform, then confirm those rules are enforced.

Include maintenance access in that conversation. Otherwise, an approved design can gradually change as people add exceptions to solve service problems.

Is cloud access control more secure than on-premises?

Neither architecture is automatically more secure. Cloud and on-premises access control place different responsibilities on your team and the provider, so compare how each proposed system handles identity, updates, data, availability, and recovery.

A cloud platform may reduce local server administration. An on-premises platform may give your team direct control over the server environment. Both need someone accountable for the work that remains.

What to review in a cloud platform

Request the provider’s security documentation and confirm how it handles encryption, software maintenance, backups, incident notification, and service availability. Review data location and sub-processors where your vendor review policy requires them.

Your organization still needs to manage administrator permissions, credential policies, integrations, and local equipment. Confirm which logs you can access and export, including administrative activity.

What to review in an on-premises platform

Identify who maintains the operating system, database, application, and service accounts. Check patching responsibilities, remote administration, backup protection, monitoring, and physical access to the server or appliance.

Ask for evidence of a recovery test. A backup file only becomes useful when your team can restore the system from it.

Does cellular access control avoid the corporate network?

Cellular access control can use a separate connection instead of the local corporate LAN when designed that way. This can simplify deployment at distributed sites, but the devices, management platform, accounts, and support connections still require cybersecurity controls.

The distinction is useful when a location has limited network availability or coordination with local IT would delay installation.

A practical example from retail

In our national retail access control deployment, Alen used Brivo cellular modules to connect locations independently of the retailer’s corporate or store network. The project paired that architecture with centrally managed credentials and regional administration.

That example shows how connectivity can fit the customer’s operating environment.

Check reliability and ownership

Before approving cellular, verify coverage, signal strength, antenna placement, and the effect of the building’s construction. Establish who owns the data plan, who receives connection alerts, and what happens if service is interrupted.

Confirm any connection to other networks or integrations, too. The architecture diagram should reflect the entire installed system.

How do you secure readers and credentials?

Review credential technology and reader-to-controller communication separately. A secure credential needs compatible equipment and sound enrollment practices, while the connection from the reader to the controller needs its own protection.

A statement that “the system is encrypted” should identify exactly which connections it covers.

Verify OSDP Secure Channel

Open Supervised Device Protocol, or OSDP, supports two-way communication between readers and controllers. Its Secure Channel mode encrypts the data exchanged over that connection.

SIA’s February 2026 OSDP implementation checklist recommends enabling Secure Channel and validating that communication works as intended. OSDP support alone doesn’t confirm that Secure Channel is configured and active.

Ask your integrator to confirm reader and controller compatibility, relevant firmware versions, key management, and commissioning test results. Check OSDP Verified status where it forms part of your purchasing requirements.

Plan credential changes around existing equipment

Document which cards, fobs, or mobile credentials you issue, how they’re enrolled, and how lost credentials are revoked. If cloning resistance is a requirement, ask the manufacturer to explain the protections in the proposed technology and configuration.

For a phased upgrade, confirm which existing readers support the new credentials. Your commercial access control design should account for daily use at every affected location, including employees who move between sites.

Who maintains software and controls remote support?

Assign responsibility for updates and vendor access before the system goes live. Each supported component needs an update process, and every remote support connection needs approved authentication, permissions, and logging.

This is easier to settle during planning than during an urgent service call when a location can’t open on time.

Track updates and end of support

Keep a record of firmware and software versions, support dates, and available security advisories. Confirm whether updates happen automatically, require scheduling, or need a technician.

Ask the manufacturer how it receives vulnerability reports and notifies customers. For unsupported equipment, document the exposure, any temporary controls, and a replacement plan with an owner.

Make vendor access visible and revocable

Find out how the integrator connects, whether access stays available between service calls, and whether you can disable it. Require named accounts, appropriate permissions, MFA where supported, and records of support activity.

Keep remote access instructions with your support documentation. The person authorizing a service visit should understand what access they are granting and when it ends.

What should IT check in integrations and logs?

For each integration, document the data exchanged, authentication method, permissions, and failure handling. For logs, confirm which events are captured, how long they remain available, and who reviews alerts.

Connecting access control to an identity system, HR platform, visitor system, or video platform can reduce manual work. It also introduces dependencies your team needs to understand.

Test the employee departure process

Follow an example employee through the full process: the departure is recorded, the integration sends the change, the access control platform processes it, and the affected controllers receive it.

Confirm whether disabling an identity account also removes physical access in your specific configuration. Those actions aren’t automatically equivalent.

Document where integration secrets are stored, how credentials are rotated, and who investigates a failed update. An integration should have only the permissions needed for its task.

Capture changes as well as door events

Access events tell you when credentials were presented. Administrative logs help explain who issued a credential, changed a permission, altered a schedule, or sent a remote door command.

Confirm retention, export options, time synchronization, and compatibility with your monitoring platform if required. Assign an owner to review alerts and respond to unexpected changes or connection failures.

What happens when access control goes offline?

Offline behavior depends on the platform, controller, configuration, and type of outage. Some controllers continue using locally stored permissions and schedules, while new changes or remote commands may not reach them until connectivity returns.

Review loss of internet connectivity, a cloud service interruption, server failure, controller failure, and power loss separately. They don’t necessarily produce the same result.

Test credential changes during an outage

Suppose an employee’s credential is revoked while one location is disconnected. If that controller relies on an older local permission record, the change may not take effect there until communication returns.

Ask how your system handles that situation, how administrators see the disconnected site, and what local response is available. Test new credentials, schedule changes, and event storage as well.

Separate door continuity from platform recovery

Door continuity covers what keeps operating locally. Platform recovery covers restoring management, configuration, records, and failed equipment.

Confirm provider recovery commitments for cloud systems and tested restoration procedures for on-premises systems. Document how a failed controller is replaced and configured. Have qualified personnel verify power-loss and emergency-release behavior as part of the approved door design.

What should a multi-site access control cybersecurity checklist include?

Use one checklist across locations, with evidence and an owner for each requirement. Record exceptions so an older site or unusual connection doesn’t disappear from view after the initial review.

Review areaEvidence to request
ArchitectureCurrent diagram, inventory, data flows, and site exceptions
Administrator identityIndividual accounts, MFA settings, role permissions, and offboarding process
NetworkApproved traffic rules, segmentation, and inbound/outbound requirements
Readers and credentialsSupported technology, Secure Channel configuration where used, and revocation process
Software lifecycleVersions, update ownership, support dates, and security notification process
Remote supportApproved accounts, access duration, authentication, and activity records
IntegrationsPermissions, secret management, data flows, and failure handling
MonitoringEvent coverage, retention, export options, and response ownership
Continuity and recoveryOffline test results, backups, restoration procedures, and controller replacement plan
Physical installationSecured equipment locations, enclosure access, and current site records

For a manageable first review, take these five steps:

  1. Collect the diagram and inventory. Identify missing information and sites that differ from the approved design.
  2. Review administrator and support accounts. Confirm ownership, permissions, MFA, and whether each account is still needed.
  3. Validate connections and integrations. Compare the installed configuration with the approved requirements.
  4. Test failure and recovery scenarios. Include off-boarding during an outage and restoration after equipment failure.
  5. Assign corrective work. Record each finding, its priority, its owner, and how you’ll confirm it’s resolved.

Build these requirements into your <a href=”https://alensecurity.com/blog/how-to-standardize-access-control-across-multiple-locations-when-every-site-is-different/” target=”_blank” rel=”noopener noreferrer”>multi-site access control standard</a>. That gives new locations a consistent starting point and makes future changes easier to review.

Frequently asked questions about access control cybersecurity

Does a physical security integrator need to work with IT?

Yes. Connected access control needs coordination between the integrator, IT, and the people responsible for building security. IT should review network connections, administrator identity, integrations, remote support, and maintenance responsibilities. Agree on those requirements before installation so the finished system fits your company’s technology policies and operating needs.

Should access control be on its own VLAN?

A dedicated VLAN may be appropriate when it supports your company’s segmentation design. The security benefit depends on the rules controlling communication between networks, along with authentication and monitoring. Review the platform’s traffic requirements and integrations before deciding how to separate it from other business systems.

Is OSDP always encrypted?

No. OSDP supports encrypted reader-to-controller communication through Secure Channel, but support for OSDP doesn’t confirm that Secure Channel is active. Verify compatibility, configuration, key management, and commissioning results. SIA recommends using Secure Channel to protect the data exchanged between readers and controllers in an OSDP deployment.

Does disabling an employee account immediately disable their badge?

It depends on the integration and whether the affected controllers can receive the change. Disabling a corporate identity account doesn’t prove physical access has been removed. Confirm the integration’s behavior, check synchronization status, and define how your team handles credential revocation at locations that are temporarily offline.

Do older access control systems always need replacement?

No. Age alone doesn’t establish the need to replace an access control system. Review support status, available security controls, integration requirements, and maintenance options. Replacement becomes a stronger consideration when equipment is unsupported or cannot meet your requirements, especially when temporary controls leave gaps your organization cannot accept.

Get clear answers about your access control system

Alen Security works with commercial organizations on access control design, installation, integration, and ongoing service. We can work with your IT and Security teams to review the existing environment and plan a system that fits how your locations operate.

Bring your site list, available system documentation, and the questions your team hasn’t been able to resolve. Whether you’re supporting a New Jersey office or a national portfolio, a clear design and a long-term service relationship make the next decision easier.

Talk with Alen Security about reviewing your access control architecture and IT requirements.


Related reading

About Alen Security

Alen Security is a commercial security company based in Cranbury, New Jersey. The company designs, installs, and services access control, video surveillance, and other commercial security systems, including solutions for organizations with multiple locations.

How to Standardize Multi-Site Access Control

How do you standardize multi-site access control?

Multi-site access control becomes hard to manage when each office uses a different platform, credential policy, and service process. One site inherits a landlord’s system. Another is added through an acquisition. A warehouse installs readers during a rushed repair. Soon, your team needs three calls to answer who can enter Site 27.

A workable standard sets one management model across locations: who grants access, which credentials are approved, how systems connect securely, what each site documents, and who supports a failed door. The hardware can vary when a building calls for it. The rules and ownership stay clear.

Start by inventorying your sites and defining the target model. Then pilot it at a few different buildings, record approved exceptions, and migrate in phases. This guide shows what to put in the standard and how to make it useful for IT, Security, Facilities, and local teams.

Employee uses a card reader at a commercial entrance in a multi-site access control system

Why do access control systems become fragmented across multiple locations?

Access control systems usually fragment as companies grow and local teams make decisions without a shared plan for the future. Common causes include:

  • Acquisitions
  • Regional purchasing
  • Landlord-provided systems
  • Different construction partners
  • Local IT ownership
  • Equipment installed before a corporate standard existed
  • Products reaching end of life at different times
  • Different industries or occupancy types across the portfolio
  • Emergency replacements that became permanent

None of these causes are unusual. The problem starts when a company keeps adding locations without deciding what the future environment should look like.

The U.S. General Services Administration (GSA) has faced the same enterprise challenge at a much larger scale. Its current Physical Access Control Systems directive describes an agency-wide approach to updating, procuring, and installing PACS while migrating disparate systems toward an enterprise environment.

A private company does not need federal requirements to use the same principle: define the enterprise model before each site solves the problem on its own.

What should a multi-site access control standard include?

The standard should answer everyday operating questions before it lists products.

A multi-site access control standard should define what every location needs to support, how teams should install and manage the system, and what happens when a site needs an exception. It should cover daily administration, equipment, security requirements, documentation, and ongoing support.

Think about the questions that land on your desk. Can you remove someone’s access across every location? Can a local manager issue a badge without getting access to the entire company? What keeps working if a site loses its internet connection? Your standard should give everyone clear answers.

Define what every location needs to support

Start with how your team needs the system to work each day. Once you agree on those expectations, you can choose equipment and configurations that support them.

  • Central visibility: Define what your team needs to see across locations, including access events, equipment status, and alerts. Someone supporting multiple sites should know where to look when a local manager reports a problem.
  • Remote administration: Specify which tasks authorized staff should be able to handle remotely, such as updating schedules or changing access permissions. That helps your team understand when it can resolve a request from its desk and when someone needs to visit.
  • Consistent credential policy: Set company-wide rules for issuing, replacing, and removing cards or mobile credentials. Employees and local managers should know what to do when someone joins, leaves, or loses a badge.
  • Defined offline operation: Spell out what must keep working when a location loses connectivity. Include how the system handles existing credentials, schedules, stored events, and updates that cannot reach the site during an outage.
  • Central user deactivation: Define how your team removes a person’s access across the locations they can enter. Include how it confirms the change and handles sites that are temporarily offline.
  • Role-based administration: Match administrative permissions to job responsibilities. A local manager may need to issue credentials for one office, while corporate security needs broader control across the portfolio.

Set consistent rules for events, doors, and support

Your team also needs to understand what the system reports and how to respond. An alert or service request should provide enough information to start working on the problem.

  • Standard event naming: Use consistent names for events and alerts wherever the platform allows. Your team should be able to recognize the same type of issue across sites without learning a different set of labels at each location.
  • Documented door hardware: Require a record of the reader, lock, controller connection, and related hardware at each opening. That gives the service team something useful to work from before it arrives.
  • A repeatable service process: Define how people report problems, who takes ownership, and when to escalate a request. Local managers should know whom to contact without calling around to find the right vendor.
  • Minimum reader security requirements: Set the minimum security capabilities and configuration requirements for readers. Different locations may need different physical devices, but every approved reader should meet the requirements that apply to its use.
  • Access event retention: Specify how long the company keeps access events and who can retrieve them. Your team should know whether the records it needs will still be available when someone requests a review.

These expectations can stay consistent even when one location uses wired readers and another uses wireless locks. The equipment can vary within the standard while supporting the same company requirements.

Define the approved equipment and system architecture

Once you know what the system needs to do, document the approved technical approach. This gives your installers, IT team, and service partners a shared starting point for each project.

  • Platform architecture: Define the approved system architecture and how sites connect to it. Document where management happens, what runs locally, and which responsibilities fall to the company or its service partners.
  • Approved controllers: Identify the controller families your organization supports and where each is appropriate. That helps teams make consistent choices during new installations, expansions, and replacements.
  • Reader technologies: Specify the approved reader technologies and communication methods. Include the capabilities needed for your credential policy and the conditions where teams may use different reader types.
  • Credential policy: Turn your company-wide credential rules into installation requirements. Teams should know which credentials the equipment must support before they order readers for a new site.
  • Door monitoring: Define which door conditions the system needs to monitor and how it should report them. Include expectations for events such as a door held open or forced open, where applicable.

Establish network, cybersecurity, and integration requirements

Access control needs coordination with the teams responsible for your network, identities, and connected systems. Document those requirements early so they become part of the project.

  • Network requirements: Specify the connectivity, addressing, and firewall requirements for the approved system. Give IT the information it needs to prepare a site and support it after installation.
  • Cybersecurity requirements: Set expectations for authentication, permissions, encryption, updates, logging, and remote support. Each location should follow the same approved security requirements wherever they apply.
  • Administrator roles: Document who can administer the system and what each role can change. Include responsibility for approving permissions and reviewing whether people still need them.
  • Identity integrations: Define how access control connects with your organization’s identity systems, where applicable. Make it clear which system supplies user information and how teams handle changes or failed updates.
  • Video integrations: Specify where access events should connect with video and what users need to see. Your team should understand which integrations it supports and how to find the relevant camera view.

Make installation and documentation repeatable

A standard needs to guide the work at the site, too. Clear installation and documentation requirements help your next project build on the last one.

  • Naming conventions: Set consistent names for sites, doors, readers, controllers, and events. Someone supporting the system remotely should be able to identify the location and equipment without asking what “Back Door 2” means.
  • Site documentation: Require current floor plans, equipment records, panel locations, photos, and as-built changes. Define where teams store those records and who updates them when work changes the installation.
  • Installation practices: Document expectations for mounting, cabling, labeling, power, and coordination with door hardware. Give installation partners a clear definition of the work your company expects.
  • Testing and acceptance: Define what teams must test before they hand over a site and who signs off. Include the functions the location needs to support, with a record of any unresolved issues.

Plan for maintenance and site exceptions

The standard should keep helping your team after the project closes. Equipment needs service, buildings change, and some sites will need an approved variation.

  • Service and preventive maintenance: Define service responsibilities, maintenance activities, and how teams record completed work. That gives your company a consistent process for supporting equipment throughout its life.
  • Exception handling: Set a process for documenting a requirement a site cannot meet, the reason, the approved alternative, and who authorized it. Include whether the exception is temporary and when someone should review it.

A technician should be able to arrive at the next location with a clear understanding of your company’s approach, even if they have never worked at that particular site.

How do you apply a multi-site access control standard to different buildings?

Group sites by how people use them. A company can set repeatable patterns for each site type without forcing every building to use the same door schedule.

Group sites by type

Corporate office: Typical needs include lobby access, employee entrances, executive areas, server rooms, conference spaces, parking, and visitor workflows.

Warehouse or distribution center: Typical needs include employee entrances, dock areas, exterior gates, cages, high-value storage, and 24-hour operations.

Retail location: Typical needs include back-of-house access, manager areas, stock rooms, finished interiors, and limited local IT infrastructure.

Manufacturing site: Typical needs include shift changes, production entrances, maintenance areas, exterior doors, overhead bays, contractor access, and closer coordination around shutdown windows.

Standardize the management model

For an IT Director or Head of Security, the largest benefit may come from consistent administration rather than identical readers. Define:

  • Who owns the platform?
  • Who can create users?
  • Who can change access groups?
  • Can regional managers administer only their region?
  • Can local managers issue temporary credentials?
  • Who approves access to restricted areas?
  • Who reviews stale accounts?
  • How are emergency changes handled?
  • How are audit logs retained?

Multi-site administration often requires delegation. One corporate administrator may not be the right person for every routine request. Giving every local manager broad access to the whole system creates a different risk.

Map administrative rights to job responsibilities. This follows the identity-governance principle of giving people the access they need and reviewing it over time. NIST SP 800-53 includes controls for least privilege and periodic review of user privileges.

Set one credential policy

A multi-site company should decide what an employee credential means across the organization. Answer these questions:

  • Will one employee credential work at every location they are authorized to enter?
  • Are mobile credentials supported?
  • Do some workers still need physical cards?
  • How does the company handle contractors?
  • What happens when someone loses a phone?
  • What happens when someone loses a card?
  • How quickly should terminated employees lose physical access?
  • Which credential technologies are approved?

Credential choices affect readers, enrollment, identity integration, support, and the employee experience. Set the policy once instead of letting each location invent its own answer.

Define reader and controller requirements

Set requirements for the equipment without locking the company into one opening type. The standard can specify:

  • Approved controller families
  • Approved reader families
  • OSDP support where required
  • OSDP Secure Channel expectations
  • Mobile credential compatibility
  • Environmental ratings for exterior readers
  • Firmware support requirements
  • Backup power requirements
  • Enclosure standards

SIA’s OSDP standard gives organizations a vendor-supported path for supervised reader communication. SIA’s 2026 implementation checklist recommends verified devices and Secure Channel where OSDP is deployed.

These requirements can become part of the enterprise standard without requiring the same physical reader at every location.

Decide when existing hardware can stay

Standardization does not always require immediate replacement. A company with 80 sites may keep compatible existing controllers until a site is renovated, as long as it sets a clear rule. For example:

  • New sites: deploy the target standard.
  • Renovated sites: migrate to the target standard.
  • Existing sites with an unsupported platform: prioritize migration.
  • Existing sites with supported hardware: retain it until a planned upgrade.
  • High-risk doors: accelerate reader or credential changes.

A clear transition rule lets the company avoid a giant one-time replacement project as the only path to consistency.

How do you document and support multi-site access control?

Six months after installation, a door stops unlocking. Your team needs to know which reader serves it, where the panel sits, and what hardware was installed. If those answers live in someone’s inbox, a routine service call turns into hours of detective work. Clear site records and a repeatable support process make the next call easier.

Your access control standard should give every location a consistent way to name equipment, maintain records, follow cybersecurity requirements, and prepare for outages. That gives your team somewhere to start when something goes wrong.

Standardize naming and site records

“Back door” may make sense to the supervisor on site. It tells an IT director supporting 30 locations very little. Give each opening and device a unique name that matches the floor plan, platform, and service record.

  • Site code: Each location should use a unique identifier, by using them consistently in the access control platform, service tickets, and site records you’ll improve standardization. A quick check with you team is can they tell which location a record belongs to at a glance. If not your site code needs some additional work.
  • Building: Identify the building when a site has more than one. The main office and the warehouse may share an address, but a technician still needs to know where to go.
  • Floor: Include the floor or level so someone can find the opening without searching the building. Use consistent labels for basements, mezzanines, and other areas that might otherwise get different names.
  • Door name: Provide each controlled opening a clear, unique name that matches the floor plan and system records. “Site 27, Warehouse, Employee Entrance” gives your team more to work with than “Door 4.”
  • Door function: Record what the opening serves, such as an employee entrance, server room, loading area, or restricted storage room. That context helps your team understand how people use the door.
  • Reader name: Identify each reader and the door it serves. If a door has readers on both sides, make it clear which one controls entry and which one controls exit.
  • Controller name: Give each controller a unique name and record the doors it manages. When a controller goes offline, your team needs to know which openings may be affected.
  • Camera association: Note which camera, if any, covers the opening. That helps someone reviewing an access event find the relevant view without clicking through cameras across the entire site.
  • Alarm input name: Label each monitored input by its location and purpose. Someone receiving an alert should be able to understand what triggered it without first looking up what “Input 7” means.

Document what your team will need during a service call

Clear names help your team find the right equipment. Site records explain what’s there, how it connects, and what has changed. Keep those records somewhere the people responsible for support can actually find them, and make updating them part of the work whenever equipment changes.

When creating the document don’t miss out on these key areas:

  • Floor plans: Mark controlled doors and relevant equipment locations on a current plan. A technician should be able to use it to find the opening and understand where it sits within the building.
  • Panel locations: Record exactly where each panel is installed, including the room or closet. “Second-floor IT closet, north wall” saves someone from opening every utility room in the building.
  • Controller models: Record the manufacturer and model of each controller. That gives your team the equipment details it needs when checking compatibility, planning upgrades, or arranging a replacement.
  • Reader models: Identify the reader installed at each opening. Readers can look similar while supporting different credentials or communication methods, so appearance alone won’t tell your team what it needs to know.
  • Lock types: Record the type of locking hardware at each controlled door. A technician preparing to service an electric strike needs different information than someone working on an electrified panic device or magnetic lock.
  • Cabling: Document cable types, labels, and known routes between equipment. Your team should have a starting point for tracing a connection without having to rediscover how the installation was wired.
  • Egress devices: Identify the devices involved in allowing people to exit, including their locations and connections where documented. These details help the service team understand the opening before making changes.
  • Power supplies: Record which power supply serves each controller or locking device and where it is located. When equipment loses power, that connection helps narrow the troubleshooting process.
  • Battery dates: Record battery installation and replacement dates. That gives the team a maintenance history it can use instead of guessing how long a battery has been in service.
  • Network details: Document the network information your authorized IT and service teams need to support the system, such as device addresses, switch ports, and VLAN assignments. Keep sensitive information in the appropriate restricted records.
  • Photos: Include clear photos of panels, equipment labels, wiring, and door hardware. A useful photo can help a remote technician understand the installation before anyone makes a trip to the site.
  • As-built changes: Update the records to show what was actually installed and what changed afterward. If a controller moved or a door received different hardware, the documentation needs to reflect that.

These records become especially useful when you need to troubleshoot a door, plan an upgrade, or schedule maintenance across several locations. Alen’s current national AEC engagement includes documenting controllers, reader modules, readers, cabling types, and egress devices during site service. The case study explains how those records support future troubleshooting, upgrades, and maintenance.

Put cybersecurity requirements in the standard

Cybersecurity should not depend on which region installed the system. The enterprise standard should address:

  • Administrator authentication
  • Multi-factor authentication
  • Role design
  • Network connectivity
  • Inbound and outbound firewall requirements
  • Encryption
  • Reader communication
  • Remote support
  • API access
  • Logging
  • Software and firmware updates
  • Vulnerability notifications
  • Vendor account governance
  • Backup and recovery

NIST’s Zero Trust Architecture warns against trusting a system solely because it sits on an internal network. A controller on the corporate LAN still needs proper identity, configuration, updates, and monitoring.

A cloud platform is not secure just because it is cloud-managed. Define the organization’s security review criteria for every architecture.

Define how each site behaves during an outage

The company needs to know how each location operates when connectivity fails. Require the selected platform to answer:

  • Do authorized credentials continue working?
  • How long can the system store events locally?
  • Does it maintain schedules?
  • What happens to a newly terminated credential during an outage?
  • Can administrators still make local changes?
  • What happens after power loss and restart?
  • Do certain facilities need redundant internet or cellular connectivity?

Different sites may need different levels of resilience. A corporate office may tolerate a short delay in new credential updates. A 24-hour distribution center may need a different plan. Set those tiers before an outage happens.

Coordinate access control with life safety

An access control standard should never replace local code review. The 2024 International Building Code has different provisions for electrically locked egress doors depending on the locking arrangement and occupancy. UL’s access and egress control guidance explains why teams must coordinate electric locking with egress behavior, power loss, panic hardware, and life-safety systems where applicable.

A corporate standard can set a repeatable review process:

  • Require a door and hardware review.
  • Identify fire-rated openings.
  • Confirm panic hardware conditions.
  • Coordinate fire-alarm release where required.
  • Document the approved locking arrangement.
  • Require final local review where applicable.

Local requirements, occupancy, door use, fire rating, lock type, and the Authority Having Jurisdiction determine the final compliant configuration. A corporate standard should require a repeatable review, not assume that one locking detail works everywhere.

How do you pilot a multi-site access control standard?

Pilot the standard before applying it across the portfolio. A small test gives the organization a chance to find problems before they repeat at every site.

Test at pilot sites

Do not publish a 70-page corporate standard and roll it out to 100 locations without testing it first. Use pilot sites to check:

  • Does the naming convention work?
  • Can the service team troubleshoot the system?
  • Can local managers do the tasks assigned to them?
  • Are identity groups mapped correctly?
  • Is the credential process understandable?
  • Does the hardware fit real door conditions?
  • Are teams capturing documentation correctly?
  • Does offline behavior match expectations?
  • Are alerts useful or too noisy?

Revise the standard before scaling it.

Document every exception

Every multi-site standard will encounter a building that cannot meet every requirement. A historic door may not accept the preferred hardware. A landlord may control the lobby system. A remote site may lack reliable broadband. A warehouse gate may need specialized equipment.

Exceptions are not a failure. Undocumented exceptions are.

For every exception, record:

  • The requirement the site cannot meet
  • Why it cannot meet it
  • The approved alternative
  • The security impact
  • The support impact
  • Who approved it
  • Whether it is temporary or permanent

This keeps exceptions from quietly becoming a second standard.

How does Alen approach multi-site access control standardization?

When working with a national architecture, engineering, and construction firm with roughly 140 offices they used Alen Security as their single point of contact for a phased Brivo roll-out. We made a 2026 case study about this client’s experiences, which included completing 50 locations.

Alen coordinates deployment with each office’s construction and renovation schedule, uses repeatable configurations, and maintains site records for future support. The client has one point of contact as the program expands. That is how a standard becomes a practical service model across locations.

Frequently asked questions about multi-site access control

Does every location need the same access control system?

A company should aim for a consistent management and security model, but every opening does not need identical hardware. Site type, door condition, occupancy, environment, and business use can call for approved variations.

Can we standardize access control gradually?

Yes. Many organizations apply the target standard to new construction, renovations, end-of-life replacements, and priority sites first, then migrate the rest over time.

Can acquired companies keep their existing access control system temporarily?

Yes, if the organization documents the risk, administration, support, and migration plan. It should define whether the existing system is a temporary exception or a permanent environment.

Should IT own enterprise access control?

Ownership varies by company. IT should usually be involved in identity, cybersecurity, networking, vendor risk, and integrations. Security or Facilities may own daily physical access operations. The standard should make those responsibilities explicit.

What should be documented at each location?

At a minimum, document door names, panel locations, controllers, readers, locks, egress components, power supplies, cabling, network requirements, credential behavior, integrations, photos, and as-built changes.

Ready to turn local systems into one operating model?

You do not need every site to look the same. You need every site to fit a plan.

For Alen, Trusted… Everywhere means that the standard stays dependable across the locations where your business operates, without pretending every building is identical.

Alen Security can review your current portfolio, identify common patterns and exceptions, and help define a multi-site access control standard that your IT, Security, Facilities, and service teams can support.

Talk with Alen Security about multi-site access control standardization.

person-using-access-control-on-their-phone

How to Replace Manual Visitor Logs in Commercial Lobbies

Manual visitor logs look harmless until you need them to answer a real question. Who is in the building right now? Did the contractor leave? Which host approved the visit? What door did the guest use? A clipboard can collect a name, but it cannot reliably manage the visit.

The right replacement is a digital visitor management system connected to your commercial access control process. It should register the guest, verify the visit, issue time limited access when needed, notify the host, and record when the visit ends. For companies with several buildings, the same system should apply one policy across every location while giving authorized teams one place to review activity.

Replacing manual visitor logs gives reception, facilities, security, and IT one consistent process for approving and recording visits.

What You Need to Know

Paper logs depend on handwriting, memory, and manual follow up.

A digital system can connect preregistration, check in, badges, host alerts, temporary credentials, and check out.

Visitor records should follow a written policy for collection, access, review, retention, and deletion.

Access control and video can add door activity and visual context to the visitor record.

Multi location organizations should use one standard process that can still account for site needs.

Why Do Manual Visitor Logs Break Down in Commercial Lobbies?

Manual visitor logs break down because they record fragments of a visit instead of controlling the full visit. Entries can be incomplete or hard to read. Guests may forget to add a departure time. Reception staff may need to call or message hosts one by one. A visitor can receive a paper badge that never expires and leave it behind for someone else to find.

The problem gets larger across several locations. One lobby asks for a name and company. Another asks for the person being visited. A third does not record departures at all. When an IT or security director needs a report, each location sends a different spreadsheet, photo, or scanned page.

Paper can also expose information to the next person who signs in. Names, employers, arrival times, and host names may sit in plain view. Moving to a digital system does not remove the need for sound data handling, but it gives the organization better control over who can see records and how long they are kept.

Alen has seen the difference in the field. For a large urban office building, our team installed access card readers, electric locks, an intercom, and visitor management software. The finished system gave the client a central visitor database, preregistration, badging, arrival alerts, photo records, ID scanning, watch lists, and reporting tied to access control. The result was documented visitor tracking within the same building entry process. Read the office building access control case study.

What Records Should Replace Manual Visitor Logs?

A visitor record should identify who arrived, why the person is there, who approved the visit, when the visit began, and when it ended. The exact fields should match the building, risk level, and company policy.

The National Institute of Standards and Technology provides a useful reference point. Its PE-8 visitor access records control calls for organizations to maintain visitor records for a defined period and review those records on a defined schedule. NIST describes records that can include the visitor’s name and organization, identification, date, entry and departure times, purpose, and the person visited.

That does not mean every lobby should collect every possible field. Collect what you need for a stated business, safety, or security reason. Then decide who can access it, how often it is reviewed, how long it remains available, and when it is deleted.

A sound visitor record often includes:

  • Visitor name and organization
  • Host name or department
  • Reason for the visit
  • Expected arrival time
  • Actual arrival and departure times
  • Building or site visited
  • Badge or temporary credential issued
  • Required policy acknowledgments
  • Escort requirement, when applicable
  • Notes tied to an access or safety event

The system should also show which employee created, approved, or changed a record. That audit history matters when someone asks what happened after the fact.

Why Replace Manual Visitor Logs Before an Emergency?

Digital visitor management can provide a current list of guests and contractors who checked in and have not checked out. That gives wardens and safety teams a better starting point during an evacuation than a clipboard that may still be sitting at reception.

The Occupational Safety and Health Administration says visitors should be accounted for after an evacuation and may need help leaving the building. OSHA notes that some employers use visitor and contractor sign in lists to account for people at the assembly area. It also warns that confusion can delay aid or lead to dangerous, unnecessary search efforts.

A digital list still depends on correct use. If visitors bypass reception or nobody closes old records, the list will be wrong. The system works when the building process works. Direct all guests through the approved entrance, require check in, make check out easy, and test the roll call process during drills.

Mobile credential at an access reader, part of the entry workflow that replaces manual visitor logs
Connect approved visits to temporary access credentials and a clear departure process.

What Should Replace Manual Visitor Logs?

Replace the sheet with a visitor management system that connects four parts of the visit: register, verify, grant, and close.

1. Register the visit

The host preregisters the visitor or the guest enters the required information at a lobby kiosk. Preregistration can send directions, arrival instructions, and a QR code before the visit. Walk in guests can follow a consistent on screen process.

2. Verify the person and purpose

Reception or security confirms the visitor, host, destination, and visit type. Depending on policy, the visitor may scan identification, answer screening questions, sign a nondisclosure agreement, or acknowledge building rules.

3. Grant only the access the visit requires

The system prints a badge or issues a temporary PIN or mobile credential. Access should apply only to the approved doors and time period. When visitor management connects with commercial access control, teams do not have to create one record at reception and a second record in another system.

4. Close the visit

The visitor checks out, the temporary credential expires, and the record receives a departure time. If the guest forgets, a defined exception process should alert staff or close the visit after review. The goal is a current occupancy record, not a database filled with guests who appear to have stayed for three weeks.

Brivo Visitor Management, powered by Envoy, follows this type of connected process. Its current product information lists preregistration, kiosk check in, host notifications, badges, temporary credentials, emergency roll call, configurable retention, reporting, and connections with access control and video.

Which Visitor Management Features Matter in a Commercial Lobby?

When replacing manual visitor logs, the right feature list starts with the building process. A corporate office with scheduled client meetings does not work like a distribution center receiving drivers, contractors, and deliveries throughout the day.

For many commercial properties, these capabilities deserve attention:

Preregistration: Hosts can enter expected guests before arrival and send instructions.

Guided kiosk check in: Every guest receives the same questions and policy prompts.

Automatic host alerts: The right employee receives an email, text, or app notice when the guest arrives.

Visible badges: Staff can identify approved visitors and see where they belong.

Time limited credentials: PINs or mobile credentials stop working at the scheduled time.

Central reporting: Authorized teams can search records across one site or the full property group.

Emergency roll call: Safety staff can review visitors who may still be on site.

Access and video context: Teams can compare a check in record with door activity and the related camera view when a review is needed.

Role based permissions: Reception, security, facilities, and IT can receive the access each role needs.

Retention controls: The company can define how long visitor information remains in the system.

For IT teams, system architecture belongs in the selection process too. Ask how the platform connects to the network, how data is encrypted, how administrator access is controlled, how updates are handled, and whether the design requires inbound ports or firewall holes. Alen favors cloud managed designs that avoid unnecessary network exposure and place access, visitor, and video activity in a centrally managed environment.

How Do You Replace Manual Visitor Logs Without Disrupting the Lobby?

To replace manual visitor logs, start with the process, then configure the technology around it. Use these seven steps.

Document the current visitor path. Follow a guest from invitation through departure. Record who approves the visit, what reception collects, how the host learns that the guest arrived, what access is issued, and how it is taken back.

Define visitor types. Separate clients, vendors, contractors, interview candidates, delivery drivers, and walk in guests. Each group may need different questions, access, escort rules, or visit duration.

Write the data policy. Decide what information each visitor type must provide, why it is collected, who can see it, how long it is kept, and who reviews exceptions. Have legal, privacy, HR, or compliance staff review the policy where required.

Select the connected systems. Confirm how visitor management will work with access control, badge printing, intercoms, video, identity services, and emergency procedures. Check the network design with IT before purchase.

Configure one pilot lobby. Build the workflows, test host alerts, print sample badges, issue temporary credentials, and run a mock evacuation. Include reception, security, facilities, IT, and several frequent hosts in the test.

Train the people who handle exceptions. The normal visit should be easy. Training should focus on what happens when a guest has no invitation, an ID does not match, the host cannot be reached, the printer fails, or the internet connection is unavailable.

Standardize the rollout. Use the pilot to create one approved setup for other locations. Keep policy, visitor categories, badge rules, reporting, and security settings consistent. Change site instructions only where the location truly requires it.

This is where a long term integrator relationship matters. Someone has to connect the lobby workflow with doors, credentials, intercoms, cameras, networks, policies, and ongoing service. One partner should own the handoffs so your IT director is not coordinating a kiosk company, a local locksmith, a camera vendor, and separate access control contractors at every site.

Frequently Asked Questions

What is a digital visitor management system?

A digital visitor management system records and manages guest activity through a kiosk, tablet, web form, or mobile process. It can handle preregistration, check in, host alerts, badges, temporary access, policy acknowledgments, check out, reporting, and emergency roll calls from one managed platform.

Can visitor management software work with access control?

Yes. A connected system can issue a visitor a PIN, badge, or mobile credential that works only at approved doors and during an approved time. The visit record and door activity can then appear together, which reduces duplicate entry and makes later review easier.

Is a paper visitor log a security risk?

A paper log can create risk when entries are incomplete, visible to later visitors, hard to search, or missing departure times. The amount of risk depends on the building and process. Digital records offer better permission, retention, search, and reporting controls when configured and managed correctly.

How does visitor management help with emergency evacuation?

A digital system can show which visitors checked in and have not checked out, giving safety teams a current roll call list. The list is useful only when every visitor follows the approved entry and exit process, so organizations should test it during evacuation drills.

How long should a company keep visitor records?

There is no single retention period for every organization. The company should set a period based on its security, safety, legal, contractual, and privacy needs. Keep records only as long as the stated purpose requires, limit access by role, and document the deletion schedule.

Replace the Clipboard With a Visitor Process You Can Trust

Replacing a manual log should give your team a clearer answer to a basic question: who is in the building, and why are they there?

The answer should not depend on whether someone remembered to write legibly or return to the front desk. It should come from a consistent process that registers the guest, verifies the visit, grants the right access, and closes the record when the person leaves.

For an IT director managing several locations, that same process should work from one centrally managed platform. The security design should avoid unnecessary open ports and firewall holes. The experience should feel simple for visitors, reception, and hosts. When something needs attention, one partner should know the sites, the system, and the people using it.

Schedule a consultation with Alen Security to review your lobby workflow, access control, visitor records, and multi location standards. We will help you identify where the manual process is breaking down and what a practical replacement should include.

A visitor log records a name. A sound visitor process manages the visit.

Is Brivo Access Control Right for Your Multi-Site Business?

By Alen Security

Your team may already have Brivo access control on the shortlist. Perhaps a regional manager wants to stop calling each store to revoke a badge. Perhaps a local server is aging out, or a new location needs access control without another machine in the rack. The product demo looks simple. Your job is to find out whether the complete system will stay simple after it reaches twenty sites, three shifts, and a Friday night network outage.

Brivo is a cloud-managed access control platform that can centralize doors, users, schedules, and events across locations. That can remove local management servers and make administration easier. It does not remove the physical door, controller, reader, power, network, identity, and service decisions. A sound Brivo evaluation tests those parts together, with the people who will own them after installation.

This guide is for an IT director evaluating Brivo for commercial buildings or a distributed business. It covers the questions that belong in the design meeting, the evidence to request in a proposal, and the tests to run at a pilot site. Features and editions change, and a capability in a product brochure is not necessarily included in your proposed license or compatible with your existing hardware. Have the integrator show the configuration that applies to your buildings.

IT infrastructure and access control hardware in a commercial facility
A cloud dashboard is one part of the access control system. The door, controller, network, and service plan still matter.

What should an IT director actually evaluate in Brivo?

Start with the operating model, not a feature count. Can your team issue and remove access from one place? Do site managers see only their own locations? Does an identity change reach the right doors, and can you prove when it did? Can a controller make the expected decision when the internet is unavailable? When a reader fails, does the right person know who owns the repair?

Brivo’s current product material describes centralized administration, local controller intelligence, mobile and physical credentials, integrations, and a range of security suite editions. Those are useful capabilities to investigate. The purchasing decision still depends on the exact panel, reader, credential, subscription, integration, and installation design quoted for your sites. Ask for a demonstration against your workflow rather than a generic tour of the interface.

We would make a short list of outcomes before asking for a bill of materials. Pick a new hire, a transferred employee, a departing contractor, a lost credential, an offline site, and a forced door. Follow each event from request to final report. The gaps become visible quickly. A polished dashboard cannot make up for a vague approval rule or an unsupported lock at a remote entrance.

Where does the cloud end and the building begin?

Cloud-managed access control moves central administration and some software responsibilities away from a server your team maintains. It does not mean every door decision waits on a round trip to the cloud. Brivo describes panels with local intelligence that store credentials and rules on site. The exact behavior depends on the panel, configuration, connected hardware, and the state of local power and network links.

Draw the system in plain language. The reader sees a credential. The controller evaluates it and drives an output. Door position and request-to-exit devices report status. The controller exchanges information with the cloud service over the approved network path. An administrator uses the cloud application to change permissions and review events. If video is connected, another system supplies the relevant footage. Each boundary has its own failure mode.

That diagram stops a common misunderstanding. Removing a local server does not remove controllers, power supplies, cabling, batteries, locks, switches, or service visits. It changes which component hosts management and where your team applies updates. In a proposal, separate the responsibilities of Brivo, the integrator, IT, security, and facilities. If nobody owns a failed controller’s network connection, the fact that the cloud is healthy will not open that door.

Will Brivo fit the doors you already have?

Do a door-by-door survey before treating existing hardware as a credit against the project. Record the lock type, reader, controller, door position switch, request-to-exit device, power supply, battery, cable path, fire alarm interface, and any elevator or gate connection. A door can look ordinary from the corridor and still need a different installation approach because of its hardware, frame, wiring, or required behavior during an alarm.

Reader compatibility and credential security are separate questions. An older reader may be supported through a migration path, while the card technology it reads may not meet your desired standard. Brivo describes support for multiple reader and credential types, including mobile options and paths from legacy Wiegand toward OSDP on supported equipment. That does not make every inherited card or reader suitable for continued use. Test representative hardware and ask what security compromises come with retaining it.

For a multi-site organization, the survey should show exceptions rather than hide them. One store may have a modern electrified lock and accessible cabling. Another may have a gate operator, a shared building entrance, and a landlord-controlled fire interface. A standard can still govern permissions, naming, testing, and support while the physical solution varies by site. Our access control site survey guide covers the details worth collecting before scope is set.

What network and cybersecurity review does Brivo need?

Bring IT into the design before a technician arrives with a controller and asks for a network jack. Inventory the panels, readers that use IP, gateways, management workstations, video components, and any integration service. Request the vendor’s current network requirements for the specific hardware and functions in the proposal. Document destinations, protocols, ports, DNS, time service, proxy requirements, and the process for changes.

A cloud-managed design can use outbound connections for routine management without exposing a controller or recorder directly to the public internet. That is a good starting principle, but do not accept “no firewall holes” as a substitute for a traffic diagram. Confirm the actual paths, including remote support, video, APIs, and any third-party integration. Place devices in a defined network zone and use firewall rules or access-control lists to limit movement. A VLAN alone is an organizational tool, not a complete boundary.

Then review the human access path. Require individual administrator accounts, roles matched to actual jobs, multifactor authentication where supported, a process for vendor access, and a way to remove privileges when an employee or contractor leaves. Brivo’s security material describes SSO, roles, logging, and independent assurance such as SOC 2 Type II and ISO/IEC 27001:2022. Those vendor controls support your review; they do not replace your own account governance, network policy, or incident process.

Ask who can change a door schedule, issue a mobile pass, export an access log, unlock remotely, and alter an integration. Test those roles. A regional manager may need to handle one district without seeing the whole company. An installer may need time-limited administrative rights. A finance reviewer may need reports without the ability to open a door. This is the point where a simple interface becomes a secure operating model.

How should multi-site roles and permissions work?

The first site is easy to make tidy. The twentieth exposes whether the permission model was designed or improvised. Before importing users, decide how you name sites, buildings, doors, access groups, schedules, holidays, and administrator roles. Define which rules are company-wide and which can be changed locally. A shared standard makes reporting and support easier because a “receiving door” means the same thing at every location.

Imagine a retailer with twelve stores and one distribution center. A store associate should reach the assigned store during a scheduled shift. A regional manager might need several stores. A maintenance contractor may need a back-of-house door for two days, after approval from a named sponsor. The distribution center may use different shifts and higher-consequence zones. Central administration should express those differences without giving everyone broad access everywhere.

Set a clear owner for access requests. HR can confirm employment, a manager can approve the job need, security can define the door policy, and IT can support the identity connection. Those are different decisions. If your organization already has an employee lifecycle process, connect the physical access workflow to it carefully. Our article on automating employee access goes deeper on approvals, exceptions, and failed updates.

Before go-live, review an access matrix with actual names or test personas. Transfer the store associate to another location. Give the contractor a temporary permission. Remove the regional manager’s old district. Ask a site manager what they can see and change. If the test produces a sprawling group called “All Doors,” fix the model before rolling it out.

Can identity and HR systems really automate door access?

Brivo describes identity connectors and APIs for linking access control to directory and workforce systems. That can reduce duplicate entry, but the existence of an integration does not establish your exact workflow. Determine which system creates the person, what event triggers a change, which attributes map to a site or role, and who resolves an error. Ask whether the proposed connector and features are included in the quoted edition and whether any separate service or license is needed.

Work through three cases. A new employee joins on Monday but needs building access before an account is fully active. An employee transfers to another site while retaining a temporary assignment at the old one. A terminated employee has an identity record disabled while a controller at one site is offline. These cases expose timing and exception rules that a perfect-path demo misses. The cloud may show a requested revocation while a disconnected controller has not received the change. Your procedure needs to account for that interval.

Keep a visible queue for failed provisioning and deprovisioning events. Decide how often it is reviewed, who can correct a mapping, and how the correction is recorded. Do not assume that an HR change should automatically grant every door implied by a job title. A person can have a valid corporate identity and still need separate approval for a lab, high-value cage, server room, or tenant suite.

A useful acceptance test is a complete trace: HR change, identity update, connector event, Brivo user and group change, controller receipt, door test, and audit record. Time each step under normal conditions and during a network failure. That gives the security and IT teams a defensible answer to “How quickly was access removed?” rather than a promise that everything happens instantly.

Should you use cards, mobile credentials, or both?

Brivo offers several credential approaches, including cards, mobile credentials, and digital wallet options on supported configurations. The right mix depends on your workforce and doors. A phone-based credential can reduce the work of printing and distributing cards, especially across many sites. A physical credential may still be useful for a shared device policy, a worker without a suitable phone, a visitor, or an environment where phones are restricted.

Do not equate “mobile” with a universal security upgrade. Consider reader compatibility, enrollment, device replacement, lost phones, employee privacy expectations, accessibility, battery state, and what happens when a person changes jobs. Test the actual reader and credential combination at the door, including a busy entrance where people arrive in a group. Ask whether the chosen mobile option uses an app, Bluetooth, NFC, or a wallet, and what is included in the contract.

Legacy cards deserve their own decision. A compatible card may preserve continuity during a phased cutover, but compatibility does not make an old credential resistant to cloning or suitable for sensitive areas. You can keep some doors running while migrating credentials in stages. Write down which people and doors move first, how long old cards remain valid, and how you identify a card that was never surrendered. Our legacy access control guide explains how to prioritize inherited equipment across locations.

Make the daily experience part of the pilot. A credential that works beautifully in a sales demonstration but creates a line at the employee entrance is a problem. So is a replacement process that leaves someone waiting outside for half a shift. The best credential policy is secure enough for the site and straightforward enough that people follow it.

Commercial access control readers considered for a Brivo deployment
Test the proposed credential with the actual reader and door hardware, during a normal shift.

What happens when the internet, network, or power fails?

Separate these failures. A WAN outage can leave the local controller powered and connected to its readers. A switch failure can isolate a panel even while the internet is healthy elsewhere. A power outage can affect the controller, lock, reader, and network equipment in different ways. A cloud service interruption has another effect. A single claim that a system “works offline” does not answer all four cases.

Brivo says its panels can store credentials and rules locally so doors can keep making decisions during an internet outage. Verify that behavior on the quoted panel and your configured doors. Test an existing employee credential and a credential issued just before the interruption. Then test a person whose access was removed while the site was disconnected. Document which changes wait for reconnection, how events are stored, and how you confirm synchronization afterward.

Power is a separate design task. Record the expected UPS run time for controllers and network equipment, the battery capacity of power supplies, and the behavior of every lock when power is lost. Coordinate egress and fire alarm interfaces with the building’s responsible professionals and authority. Do not promise that all doors automatically unlock on an alarm. The correct arrangement depends on the opening, hardware, applicable code, and approved design.

Run a planned failure test at a representative site before expansion. Start with a normal event log, disconnect the WAN, use several credentials, create a change in the cloud, restore service, and compare the controller and cloud records. Repeat with the relevant power and switch scenarios under a controlled test plan. Our cloud access control outage guide covers the questions to ask at each step.

How should video work with Brivo access events?

Linked video can make an access event easier to investigate. A denied entry at a side door, a door held open, or a credential used after hours becomes more useful when the reviewer can see what happened around the event. Brivo’s platform describes integrated video capabilities, but the exact cameras, recorder, storage, retention, licensing, and event mapping in your proposal need verification.

Ask the integrator to show an event at an actual pilot door. Does the clip start early enough to show the person approaching? Is the camera aimed at the right side of the opening? Are timestamps aligned? Who may see the video, and who can export it? If the network or recorder is unavailable, does the access event remain visible even when the footage does not? Those details determine whether “one dashboard” saves time in a real investigation.

Video has its own network and storage requirements. A live stream viewed remotely, an incident export, and continuous recording can place different demands on the WAN and local infrastructure. Decide where footage lives and how long it remains available. Avoid assuming that every cloud-managed camera stores locally or that only metadata crosses the network. Our guide to connecting access control and video examines where the integration earns its cost.

Access event and video review in a central security management interface
Show the event-to-video workflow at the pilot door, including permissions and export controls.

What reporting and compliance claims should you verify?

Access logs can support an investigation and an audit, but a log is not the same thing as compliance. Brivo’s own security certifications concern the vendor’s controls and assessed scope. Your organization’s obligations may require particular retention, review, access approvals, evidence preservation, and documented corrective action. Do not assume a subscription automatically produces a report sufficient for every SOC 2, HIPAA, or PCI DSS inquiry.

Start with the questions you may need to answer. Who had access to the server room on a particular date? Who approved that access? When was a former employee’s credential removed, and when did each relevant controller receive the change? Who altered a door schedule? Can you retrieve the event without granting an auditor full administrative rights? Test a sample request with your security and compliance teams.

Then set retention and export rules. Confirm what data is captured, how long your edition retains it, how exports are protected, and what happens when a site is disconnected. Align timestamps and site naming. Decide who reviews exception reports and what action follows a denied entry or held-open door. A dashboard can surface data, but a named owner must decide what to do with it.

Ask for a demonstration of a report from two sites with different local managers. If the same event has different names, time zones, or approval records, standardize those fields. Reporting gets harder as locations are added unless the design begins with a common language.

How do you compare the full cost of a Brivo deployment?

A cloud subscription can make some expenses more predictable, but it does not turn every cost into a monthly fee. Put the capital and recurring items in one view over the same planning period. Include controllers, readers, lock hardware, power supplies, cabling, network changes, installation labor, permits where required, credential issuance, subscriptions, video, integrations, training, and support. Add the cost of surveying and replacing doors that fail the pilot’s standard.

Ask for the proposed Brivo edition and license basis in writing. Which features are included? What changes when you add a door, site, user, mobile credential, video channel, administrator, API integration, or advanced report? Do different locations need different editions? Brivo publishes edition descriptions, but the proposal and contract determine the actual package and commercial terms you will receive.

Compare the current system fairly. Your existing server has costs: support time, backups, operating system updates, hardware replacement, remote access, and time spent asking a local manager to make a change. Some of those may shrink. Others move to controller maintenance, network support, subscription management, and integration monitoring. A credible business case shows what work disappears, what remains, and who will do it.

One practical method is to price a representative site first, then a standard site, then the known exceptions. Avoid multiplying the easiest store by fifty. Include the remote warehouse with a gate, the office with an elevator, and the landlord-controlled lobby. These are the places where a neat per-door estimate can fail.

Who owns Brivo after the installation?

The handoff should be a document and a working meeting, not an email that says the project is complete. IT needs the network diagram, device inventory, permitted traffic, integration credentials and ownership, monitoring method, and update process. Security needs access groups, approval rules, administrator roles, reports, and incident procedures. Facilities needs door hardware details, service contacts, spare parts, and what to do when a door fails. The integrator needs a clear service boundary.

Agree on the alert path before go-live. A controller offline at midnight is different from a reader with intermittent failures, a held-open door during business hours, or a failed identity sync. Who receives each alert? Who can diagnose it remotely? When is an on-site visit required? What happens if the issue crosses the line between IT, physical security, and building maintenance?

At Alen Security, the aim is a repeatable design and a service relationship that survives staff changes and site growth. We can survey the doors, design the access and video environment, install it, and support it. Your team should still receive enough documentation to understand what was built. A dependable partner makes the system easier to own, not mysterious.

There is a real Alen example of this operating model. In our national architecture, engineering, and construction firm case study, we document a phased Brivo program for a portfolio of about 140 offices, with 50 locations deployed at the time of publication. Installations were coordinated with construction and renovation schedules, and the relationship includes preventive maintenance and quarterly planning. The lesson is the repeatable rollout and continuing ownership, not a promise that every site can use identical hardware or move on the same timetable.

What should a Brivo pilot prove before a larger rollout?

Choose a pilot that represents your ordinary complications. It should include a high-traffic entrance, a restricted interior door, a manager who administers the site, a remote user, and at least one inherited hardware constraint. If video or identity integration is part of the purchase, include it in the pilot. A showroom installation with one clean door proves very little about the rollout you will actually fund.

Write acceptance criteria before installation. They should cover a new user, role change, termination, temporary visitor or contractor, lost credential, denied entry, held-open door, offline controller, network recovery, administrator privilege, event search, and service escalation. Have IT, security, and facilities observe the relevant tests. Record the result, exception, owner, and correction date.

Four questions should have an answer before you approve expansion:

  • Can the people responsible for daily access changes complete them without broad administrator rights?
  • Can IT verify and support every required connection without an unexplained inbound exposure?
  • Do the doors and records behave as documented during a controlled failure and recovery?
  • Can Alen and the customer’s teams identify, diagnose, and repair a failed component through an agreed service path?

After the pilot, update the standard. The first site will teach you about naming, hardware, shifts, exceptions, and training. Carry those lessons into the next location rather than copying the initial configuration blindly. A staged rollout lets the organization improve the model before small errors multiply across the estate.

How do you avoid repeating the same problems at every site?

Make a site package with room for real differences. It should define the approved controller and reader families, credential policy, network zone, naming pattern, administrator roles, access-group templates, event settings, outage test, installation documentation, and support handoff. Then create an exception record for every deviation. The standard is a way to make differences visible and manageable, not a claim that every building has identical doors.

Use the first few installations to refine the package. If a reader struggles in a metal-framed loading area, fix the specification. If a regional manager cannot find the right site in a long list, fix the naming. If a contractor’s access lasts longer than the job, fix the approval and expiration workflow. These are design lessons, not reasons to give every facility its own independent rules.

Our article on standardizing multi-site access control addresses the broader management model. This Brivo evaluation has a narrower job: prove that the proposed platform, edition, hardware, integrations, and service agreement can deliver that model in your buildings.

Frequently asked questions

Does Brivo need a server at each location?

A cloud-managed Brivo design can remove the local management server used by some older systems. Each site still needs the appropriate controllers, readers, door hardware, power, and network connection. Confirm the quoted panel architecture and any local integration or video equipment. Ask the integrator to show which devices your IT and facilities teams will support on site.

Will existing badges and readers work with Brivo?

Some may, but compatibility depends on the reader, card technology, controller, wiring, and selected configuration. Reusing a legacy credential can ease a phased migration while preserving an avoidable security weakness. Survey representative doors, test the actual credentials, and decide which hardware stays temporarily, which is upgraded, and when old credentials are retired.

What happens to Brivo doors during an internet outage?

Brivo describes local controller intelligence that can use stored credentials and rules while a site is disconnected. New permissions and revocations may not reach an offline controller until connectivity returns. Power loss and fire alarm behavior are separate design questions. Test the quoted hardware, existing and changed credentials, event storage, and recovery at a pilot site.

Can Brivo connect to our identity provider and video system?

Brivo offers identity and video integrations, but the exact connector, edition, third-party product, licensing, and workflow determine what is possible for your organization. Ask for a live demonstration using a representative hire, transfer, termination, and access event. Document what happens when the connection fails, who sees the error, and who fixes it.

How should we evaluate a Brivo proposal for multiple sites?

Compare the full system and service model, not a price per door alone. Review a representative site survey, the network and controller design, credential plan, permissions, outage behavior, integration scope, subscriptions, installation exceptions, training, and support ownership. Pilot a difficult site and require written acceptance results before using it as the template for a larger rollout.

Make the decision at a real door

A cloud platform can give an IT director a cleaner way to manage access across locations. The value is real when the day-to-day work improves: a manager can request the right access, a departing employee loses it through a traceable process, an investigator can find the relevant event, and a disconnected site behaves as expected. Those results come from a tested design and clear ownership.

If Brivo is on your shortlist, bring one complicated location to the table. Show us the doors, the inherited hardware, the network rules, the user lifecycle, and the service frustrations. Alen Security can help turn that into a scoped survey and pilot, then a standard your other locations can follow. Schedule a Brivo access control assessment and we will map what the first site needs to prove before you commit to the rest.

An access control site survey may document this mobile credential and the electronic door lock it operates.

Stuck in the Server Room? Unlock Your Freedom

You are likely reading this because you are an IT Director or a Facilities Manager who is tired. Tired of the late-night calls. Tired of the “server is down” alerts. Tired of being the only person who knows how to reboot a system that should have been retired a decade ago.

You manage warehouses, retail chains, or multi-site offices. You are accountable for uptime, compliance, and asset protection. Yet, you find yourself tethered to a physical server room, babysitting hardware that acts more like a hostage-taker than a tool.


Lower Total Cost of Ownership


AGING HARDWARE? SCALE WITHOUT LIMITS.

How do cloud-first security systems scale without adding more server room complexity?

Cloud-first systems scale by shifting management and core services away from local servers, so adding sites, cameras, and doors does not require piling more hardware into your server room. You gain a standardized platform that grows with your business instead of creating more maintenance overhead.

The traditional model of physical security relies on the NVR (Network Video Recorder) and the local access control server. These boxes sit in your server room, humming away, consuming power, and generating heat.

But what happens when you add a new warehouse? What happens when you open five more retail locations across the region?

In the old world, you buy five more NVRs. You configure five more servers. You set up five more VPNs. You create a “vendor sprawl” nightmare that makes standardization impossible.


Cloud-first systems change the math. When you move to a cloud VMS (Video Management System) or cloud-based access control, the hardware at the “edge”: your cameras and door controllers: talks directly to the cloud. There is no central server to fail. There is no hardware to outgrow.

We call this SCALABLE security. Whether you have one door or one thousand, the management interface remains the same. You add a site, and it appears on your dashboard. No new server racks required.


CYBERSECURITY CONCERNS? CLOSE THE DOOR ON OPEN PORTS.

Why is a no-open-ports architecture more secure?

A no-open-ports architecture is more secure because it avoids exposing inbound pathways into your network for remote security access. That reduces attack surface and gives your IT team more confidence that the security system is not creating unnecessary cyber risk.

For any IT professional, the term “port forwarding” is enough to cause a headache. In the legacy world, if you wanted to view your security cameras from home, you had to open a port in your firewall. You had to tell the world, “Here is a direct path into my internal network.”

This is a massive cybersecurity blind spot. Every open port is an invitation to bad actors. It is a vulnerability that requires constant monitoring, patching, and hardening.


Modern cloud systems, like the solutions we provide through partners like Eagle Eye Networks, utilize outbound-only connections. Your cameras and controllers “check in” with the cloud using encrypted, standard HTTPS ports (typically 443). Because the connection is initiated from the inside out, you don’t have to poke holes in your firewall.

This provides accountability and confidence. You can sleep knowing that your physical security system isn’t the back door for a ransomware attack.

When the time comes where you are ready to take the next step, you can look to us at Alen Security. On top of conducting an audit and installing the system, we are here for on-going training and any necessary maintenance that your system requires.

Contact us today!


FAQ: Cloud-First Security for Multi-Site Businesses

How do cloud-first security systems scale without adding more server room complexity? Cloud-first systems move video and access control management off local servers, so you add cameras and doors at new sites without adding boxes to your server room. Buy five NVRs for five new warehouses under the old model, and you also buy five servers and configure five VPNs along with them. Under a cloud model, a new site checks into the same platform and shows up on your dashboard the day you plug it in.

Why is a no-open-ports architecture more secure? A no-open-ports architecture blocks the inbound path attackers use to reach your network, because your cameras and controllers connect out to the cloud instead of waiting for a connection in. You never open a firewall port to view footage from home. Your devices check in over standard HTTPS, the same protocol your bank uses, so your team stops maintaining a hole in the perimeter to watch a parking lot camera.

What is the difference between a traditional NVR and a cloud VMS? A traditional NVR stores footage on a physical box in your server room, and your team maintains and replaces that box over its lifespan. A cloud VMS, like the Eagle Eye Networks platform, stores and manages footage in the cloud, so the hardware at each site is a camera checking in, not a recorder someone has to babysit. One login covers every site instead of one server per site.

How does moving to cloud-based security reduce IT workload across multiple sites? Cloud-based security shrinks the maintenance list at each site down to cameras and door controllers, since no local server needs patching, backup, or replacement. An IT Director running ten retail locations logs into one dashboard instead of ten separate systems, each with its own firmware version and its own late-night alert. A new location joins the same platform on day one, so onboarding takes hours instead of a hardware order and an installation project.

Does cloud-based video surveillance keep working if the internet goes down? Cloud cameras from providers like Eagle Eye Networks store footage locally on the camera during an outage, then sync to the cloud once the connection returns, so you don’t lose recordings. Live view goes offline until the connection comes back, the same way an on-premise NVR goes offline if its own network drops. You wait on an internet connection to restore itself instead of troubleshooting a server that failed.

What should IT Directors look for when choosing a cloud security provider? Ask whether the provider uses outbound-only connections, so you never open inbound ports on your firewall. Ask how the platform handles multi-site management, since a system built for one location often breaks once you add a fifth site or a fiftieth. Ask how long the provider has protected physical buildings, because a company with decades of experience treats compliance and uptime differently than a software company entering security this year.

Does switching to cloud-first security cost less than running on-premise hardware? Cloud-first security cuts the cost of buying and replacing NVRs and servers at every site, since the provider maintains that infrastructure instead of you. You stop paying for rack space and power for boxes that exist only to record video. You pay a predictable subscription instead of refreshing hardware every five to seven years, avoiding a surprise capital expense when a server fails.

Person looking at a computer screen with a green digital interface.

Can Your Access Control System Be a Cybersecurity Blind Spot?

Can an access control system become a cybersecurity blind spot? Yes. Teams can overlook it when its controllers, management software, credentials, remote support, and network connections sit outside routine IT and facilities reviews. Add the system to your asset inventory, assign an owner, protect administrator access, plan updates, monitor changes, and test recovery around door-safety requirements.

An access control system connects digital permissions to physical entry. It may include readers, controllers, management software, operator accounts, networks, cloud services, or support tools. Its design varies by site, but the questions are consistent: What is connected? Who can change it? How is it maintained? What happens if service is interrupted?

An access control system cybersecurity review can help teams identify the gaps this guide covers. It explains what to review and how IT, facilities, and security teams can coordinate the work without making door operations harder to manage.

Person at a computer with a green digital interface, used here to illustrate access control system cybersecurity.

Key takeaways

  • Include access control in the organization’s technology inventory and security review.
  • Identify system components, network connections, administrator accounts, integrations, and support paths.
  • Give IT, facilities, and security clear responsibilities, with one person accountable for the complete system.
  • Review access permissions, remote support, update status, system logs, and configuration backups.
  • Consider door operation and life-safety requirements when planning cybersecurity changes or recovery procedures.
  • Revisit the system after meaningful changes to a site, network, integration, credential policy, or support arrangement.

What does access control system cybersecurity cover?

Access control system cybersecurity is the set of technical and operational practices that protect the technology used to manage physical entry. The scope includes connected devices and software, the accounts that administer them, the communications between components, the records they create, and the maintenance procedures people use.

A door reader is only one part of the picture. Depending on the installation, other parts may include a door controller, a management server or hosted service, operator workstations, credential databases, remote-support tools, network connections, and integrations with identity or video systems. Some systems have only a subset of these components. The first task is to identify the actual design rather than assume every location is the same.

The system also has operational requirements. A door may need to follow a schedule during a temporary network interruption. Staff may need a documented way to manage entry during an outage. Emergency egress must continue to meet applicable life-safety requirements. Cybersecurity changes should account for these needs as part of system design and testing.

NIST includes physical access control systems among examples of operational technology. Its guidance recognizes that operational technology security must account for reliability, performance, and safety. That context is useful for access control: safeguards should protect the system while supporting the way a building needs to operate. See NIST SP 800-82 Rev. 3.

Why can access control become a cybersecurity blind spot?

Teams can miss access control when they treat it only as door hardware and leave its software, accounts, and network connections out of routine technology reviews. One team may install the system, another may operate it, IT may connect it, and a separate group may handle support. Without a clear handoff, useful information can remain scattered across people and records.

Common causes include:

  • Unclear ownership: No one is accountable for the system from installation through maintenance and recovery.
  • Incomplete inventory: Records show the doors but omit management services, controllers, integrations, support accounts, or network paths.
  • Unreviewed administrator access: Accounts remain active after a role changes, a project ends, or a service arrangement changes.
  • Unknown update status: Teams are not sure who receives maintenance notices, tests changes, or confirms that work is complete.
  • Limited visibility: The organization has not decided which events are logged or who reviews them.
  • Outdated diagrams: Network or site documentation no longer matches what is installed.
  • Untested recovery: Staff do not know how the system or doors behave during a service interruption.

These are coordination and lifecycle problems as much as technical problems. As a result, teams can address them more easily when the system appears in the same inventory, review schedule, and change process as other connected technology.

What risks should teams consider?

Access control system cybersecurity risks depend on the system’s design, configuration, support status, and business use. A review should identify realistic paths to unauthorized changes, service disruption, or loss of useful records, then help the team choose controls that match the organization’s requirements.

For example, weak administrator access could let someone make changes beyond their role. A team may leave an old account active after no one needs it. A network connection that teams have not reviewed could link systems they need to keep separate. Missing logs could make it harder to understand who changed a setting or when an issue began. If the team has not tested its recovery plan, it may delay a safe, coordinated response during an outage.

These examples are reasons to review the actual environment. However, they do not mean every system has the same weakness or that a connected access control system is automatically unsafe. Avoid assumptions based on the system’s age, hosting model, or product label alone. Verify support status, configuration, access practices, and operational requirements at each site.

How can you find gaps in an access control system?

A useful review starts with evidence and ends with assigned actions. Gather the current system inventory, diagrams, access lists, update records, support procedures, and recovery instructions. If something is missing, document it as a gap and assign someone to resolve it.

1. Map the system and its connections

List the sites, doors, readers, controllers, management software or service, operator devices, integrations, and support methods that are in scope. Record the owner and technical contact for each location. Note which components are centrally managed and which operate independently.

Then map the communications between those components. For each network connection, capture its purpose, direction, owner, and the required protocols or services. Compare that record with the current network configuration. Where the architecture allows, separate access control traffic from unrelated business systems and limit communication to what the installation requires. Avoid exposing management interfaces directly to the public internet.

A diagram from an earlier project is useful only if it is still accurate. Confirm it after a renovation, network change, new integration, or site expansion. A consistent record across locations makes troubleshooting and future reviews easier.

2. Review administrator and operator accounts

Create a list of administrator, operator, service, and remote-support accounts. For each account, record who owns it, why it exists, what it can do, and when it was last reviewed. Remove access that is no longer needed. Where the system supports it, use named accounts rather than shared administrator credentials so teams can tie each action to an individual.

Require multifactor authentication for privileged or remote access wherever available. Give users only the access needed for their work. Review permissions when employees change roles, leave, or move to another site. Include temporary workers and service personnel in the review process.

CISA recommends using multifactor authentication to add protection to business accounts. Its multifactor authentication guidance is a useful reference when reviewing administrative and remote access requirements.

3. Define remote support boundaries

Document every remote maintenance method. Identify who approves each session, how the system authenticates each person, which sites and settings they can reach, which activity it records, and who closes access. Prefer named, time-limited access where the system supports it instead of permanent shared access.

Agree on the process before an urgent repair requires it. Set expectations for notification, approved work windows, changes that need a second review, and who documents the work. Recheck the authorized access list when a support role or service arrangement changes.

The aim is to support timely maintenance while keeping access limited and visible. A clear process makes it easier for IT, facilities, security, and service personnel to coordinate without relying on informal assumptions.

4. Confirm updates and support status

Record the installed software or firmware versions when available, the support status of each important component, and the date of the last maintenance review. Decide who receives update notices, evaluates their relevance, tests changes, approves a schedule, and verifies completion.

Plan updates around the system’s operational requirements. Consider which sites or doors the change may affect, how the team will test it, who needs notice, and how to restore the previous configuration. Avoid installing changes without an appropriate plan, but do not leave updates without review indefinitely. If the vendor no longer supports a component, document the gap and the decision about replacement or other temporary safeguards.

5. Protect configuration and communications

Confirm how teams protect system credentials, configuration information, and communications in transit and at rest. Confirm which protocols or services are required, who manages certificates or keys when applicable, and how teams limit configuration access. Record any technical limitation and revisit it when the design changes.

Configuration exports and backups can reveal sensitive information about permissions, door schedules, site layouts, or network settings. Store them in a location the organization approves, limit access to people who need them, and maintain enough version history to recover from an unwanted change.

6. Decide what to log and who reviews it

Confirm which events the system records, such as administrator logins, credential changes, permission updates, configuration changes, failed access attempts, service interruptions, and support activity. Make sure timestamps are consistent and retention follows the organization’s policies.

Name the person or team responsible for review and escalation. Decide what activity warrants follow-up, who must report it and how quickly, and where the team will keep the record. Logs can support troubleshooting and an incident review, but only if staff know how to access and interpret them. CISA’s business logging guidance explains how records of system activity can help identify unusual events.

7. Test backup and outage procedures

Identify the configuration and operating records your team needs to restore the system. Confirm who stores the backups, who can retrieve them, how often the team updates them, and whether restoration instructions remain current. Test recovery in a planned way that does not put building operations at unnecessary risk.

Include door behavior in outage planning. Decide how staff will manage access if the network, power, or central service is interrupted. Confirm who communicates with occupants, who contacts the system owner, and who restores normal operation. Keep emergency egress and applicable life-safety requirements central to the plan.

8. Review integrations and changes

Document any connection to identity services, video, visitor processes, or other systems. For each connection, record its purpose, the information exchanged, the account or credential that connects it, the permissions it needs, and the person who owns it. Remove integrations that no longer support a business need.

Use the organization’s change process for network, account, firmware, integration, and door-schedule changes. A useful record answers: what changed, why, who approved it, how the team tested it, and how the team can restore the prior state. Notify the teams whose responsibilities or operations may be affected.

Does cloud hosting eliminate access control cybersecurity risk?

No. A cloud-hosted service changes where some systems operate and who maintains some infrastructure, but the deployment model alone does not establish that an access control system is secure. Organizations still need to evaluate administrator access, device communications, account configuration, integrations, logging, service availability, and recovery.

A hosted service may reduce some local server maintenance. However, it can also introduce dependencies on internet connectivity, account management, service availability, and the provider’s operating practices. A locally managed system may give an organization control over more of its own infrastructure, while requiring that organization to maintain it. A separate network path may reduce reliance on a business LAN in some designs, but still needs secure administration and a documented recovery process.

Ask for evidence about the controls that matter to your environment. Which safeguards protect privileged access? Which events does the system log? Who communicates and deploys changes? What happens if a site loses connectivity? What can the organization restore? Which controls does the service provider operate, and which does the organization manage?

Compare answers against how each location works. A system should be maintainable, supportable, and practical for the people responsible for it. Do not assume that one architecture is right for every building.

Who should manage the review?

IT, facilities, and security should contribute because each team understands a different part of the system. Assign one person or role to coordinate the complete review and make sure open actions are tracked.

  • IT reviews network connections, account standards, remote access, and logging requirements.
  • Facilities confirms door operation, site changes, maintenance windows, and life-safety needs.
  • Security defines access policy, approvals, credential changes, and how events are reviewed.
  • The system owner maintains the inventory, diagrams, review schedule, support contacts, and open-action list.
  • Service personnel follow approved access and change processes and document their work.

In a smaller organization, one person may perform several roles. The important thing is to document who approves changes, who performs them, and who confirms that they worked as intended. Use a second review for changes that affect many doors, privileged access, or multiple locations when practical.

NIST’s Cybersecurity Framework 2.0 groups cybersecurity work into Govern, Identify, Protect, Detect, Respond, and Recover. Those functions can help teams connect ownership, system discovery, safeguards, monitoring, and recovery. See the NIST Cybersecurity Framework overview.

When should an access control system be reviewed?

Review the system on a regular schedule and after changes that can affect how it works or who can access it. At minimum, include it in the organization’s annual cybersecurity and facilities review. In addition, review accounts and support access more often when staffing or service arrangements change.

Trigger an additional review after the organization opens a new location, redesigns a network, introduces an integration, changes an access policy, replaces equipment, or responds to an incident that affects the system. Recheck diagrams and recovery procedures after building work or a major service change. Keep the review proportional to the system’s operational importance and exposure.

Every review should end with a short action list. Record the gap, owner, due date, status, and evidence of completion. If the team cannot resolve a decision immediately, record the reason, temporary safeguard, approving role, and date for reconsideration.

What should you ask in a cybersecurity review?

Use these questions to keep the review focused on the system that is actually installed:

  • Which locations, doors, controllers, management services, and integrations are in scope?
  • Who owns the complete system and each of its technical controls?
  • Which administrator and support accounts are active, and when were they last reviewed?
  • Which network connections are necessary, and how are they limited?
  • Who evaluates, tests, schedules, and documents updates?
  • What events are recorded, who reviews them, and how are they retained?
  • How will doors and staff operate during a network, power, or central-service interruption?
  • Which records and configurations are needed for recovery, and has the process been tested?
  • What changes should trigger another review?

If an answer is unclear, document it and assign an owner. A written record reduces the chance that teams make different assumptions about the same system.

Frequently asked questions

Can an access control system create cybersecurity risk?

Yes. A connected system can create risk when teams do not manage administrator accounts, network paths, support access, software maintenance, or logs. The level of risk depends on the actual architecture and configuration. Review the installed system and its operating procedures before deciding which safeguards or changes the team needs.

Is an access control system considered operational technology?

NIST includes physical access control systems among examples of operational technology. That classification helps teams consider reliability, performance, and safety alongside cybersecurity. Organizations should review how their own doors and connected components behave during network, power, or service interruptions rather than assume every system has identical requirements.

What is the first step in an access control cybersecurity review?

Start with an accurate inventory and a named owner. List locations, controllers, management software or services, accounts, network connections, integrations, and support methods. Then verify administrator access and update status. This gives IT, facilities, and security a shared picture before they prioritize technical changes.

Does moving access control to the cloud make it secure?

No. Hosting changes where some infrastructure runs, but the organization still needs to assess accounts, device communications, integrations, logs, availability, and recovery. Ask which controls the service provider handles and which your organization manages, then document the evidence and operating process for each.

How often should access control system cybersecurity be reviewed?

Include the system in an annual review and repeat the review after a new site, network redesign, integration, equipment change, policy update, or support change. Review accounts when staff roles or service responsibilities change. Set a shorter cadence for components that have higher operational importance or exposure.

Sources and further reading